

Overview
OneCLI injects your OpenAI credentials into requests toapi.openai.com automatically. Agents make standard HTTP requests to the OpenAI API; the gateway adds the Authorization: Bearer header before forwarding.
This lets agents use GPT models, DALL-E, embeddings, and other OpenAI services without ever seeing or handling your credentials directly. For a comparison of supported LLM providers, see LLM Providers.
What you will set up
- An OpenAI credential in OneCLI: a pay-per-use API key or your ChatGPT plan through Codex OAuth
- Automatic injection of the
Authorizationheader on requests toapi.openai.com - Automatic token refresh for Codex OAuth
- Per-agent access to the key, with optional organization rules
Auth methods
OneCLI supports two ways to authenticate with OpenAI:Setup: API Key
Use this method if you have an OpenAI API key with pay-per-use billing.1
Get your API key
Go to platform.openai.com/api-keys and create a new secret key. Copy it — you won’t be able to see it again.
2
Add the key in OneCLI
Open the OneCLI dashboard, navigate to Connections > LLMs, and click Add LLM Key. Select OpenAI, make sure the API Key tab is selected, and paste your key.
Setup: Codex (OAuth)
Use this method to route requests through your ChatGPT subscription instead of paying per API call. This uses the same OAuth credentials that OpenAI Codex CLI uses.1
Install Codex CLI
2
Authenticate with device auth
~/.codex/auth.json.If you see “Please contact your workspace admin to enable device code authentication”, your ChatGPT workspace admin needs to turn on device code sign-in for Codex before you can continue.
3
Add the credentials in OneCLI
Open the OneCLI dashboard, navigate to Connections > LLMs, and click Add LLM Key. Select OpenAI and switch to the Codex (OAuth) tab. The dialog shows the two steps: run 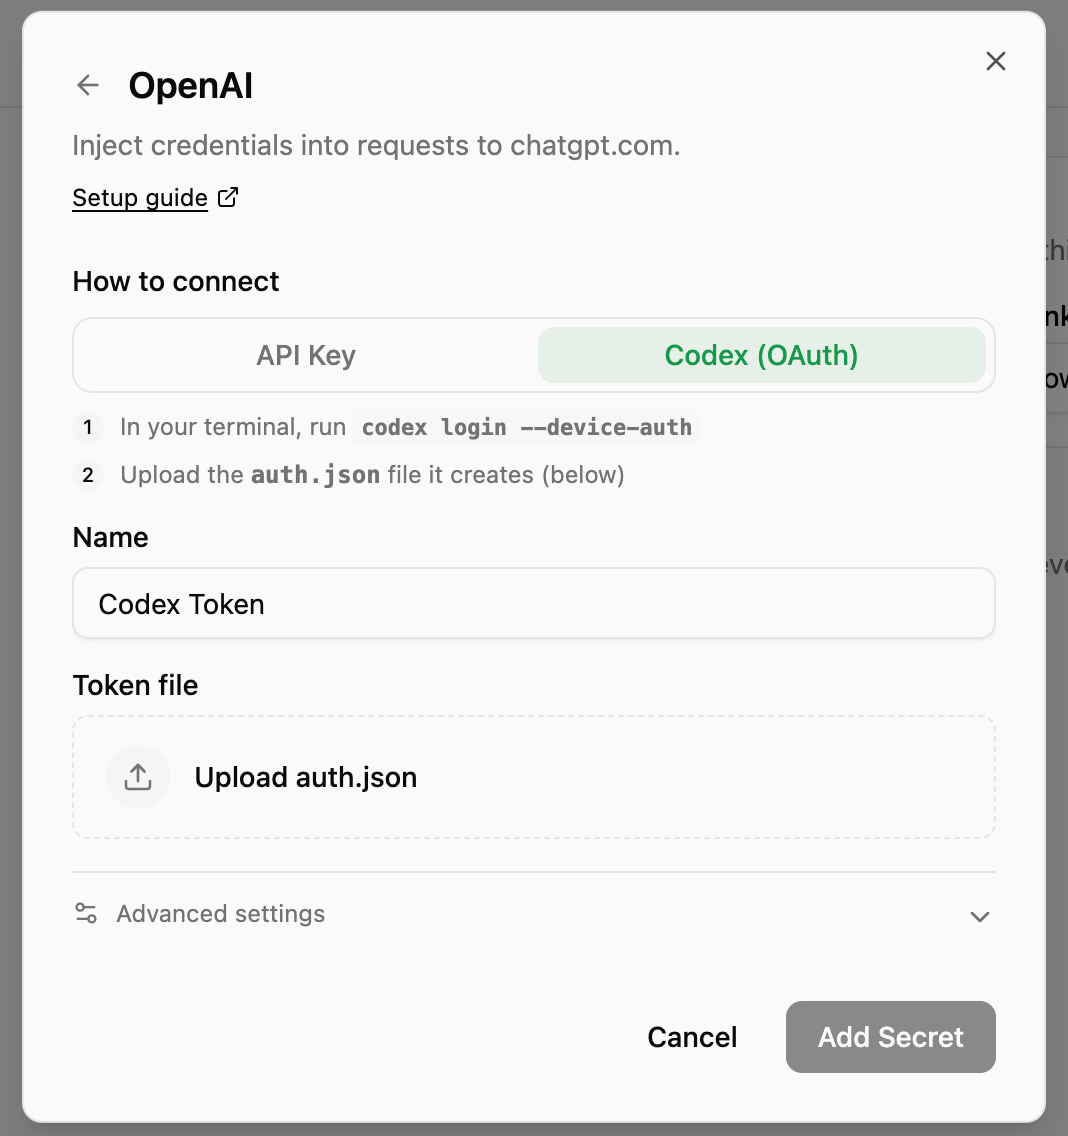
codex login --device-auth (click the command to copy it), then upload the auth.json file it creates (~/.codex/auth.json).The gateway automatically refreshes the access token when it expires using the stored refresh token — no manual re-authentication needed.
How it works
- Your credentials are encrypted and stored by OneCLI (AES-256-GCM at rest)
- When an agent sends a request to
api.openai.com, the gateway intercepts it - The gateway injects an
Authorization: Bearer {token}header - The request is forwarded to OpenAI
Controlling access
Access is per agent: attach the key to each agent that needs it — an agent without the grant can’t use it at all. Organization rules add guardrails on top: rate-limit requests, restrict agents to specific models by blocking certain paths, or flag high-cost operations for manual approval. Everything is checked before credential injection, so a blocked request never reaches OpenAI.FAQ
How do I rotate my OpenAI API key?
How do I rotate my OpenAI API key?
Create a new key at platform.openai.com/api-keys, then update it in the OneCLI dashboard. All agents pick up the new key automatically, with no changes to agent config. Revoke the old key in OpenAI afterward.
How do I keep my OpenAI key out of the agent's context?
How do I keep my OpenAI key out of the agent's context?
Store it in OneCLI instead of an environment variable or prompt. The gateway adds the
Authorization header at the proxy, so the agent never holds the raw key and can’t print, log, or commit it. See How it works.Can I use my ChatGPT Plus or Pro plan instead of API billing?
Can I use my ChatGPT Plus or Pro plan instead of API billing?
Yes. Use the Codex (OAuth) method: run
codex login --device-auth and upload ~/.codex/auth.json. Requests then count against your ChatGPT subscription.Do I need to re-authenticate when the Codex token expires?
Do I need to re-authenticate when the Codex token expires?
No. The gateway uses the stored refresh token to get a new access token and saves it, so agents aren’t interrupted. If you sign in to Codex again, upload the new
auth.json and agents use it automatically.