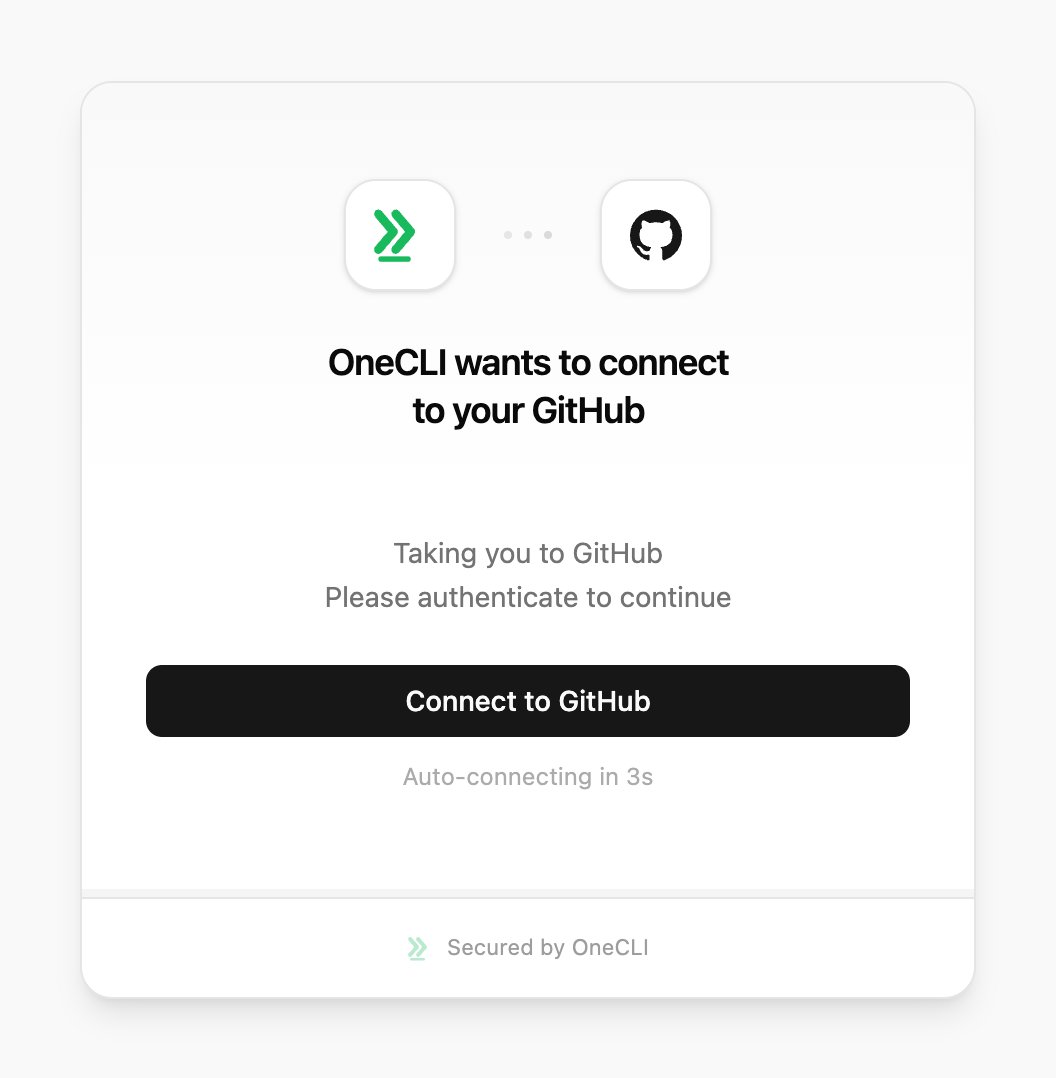
Connect GitHub with OAuth or a GitHub App so agents can push code, open PRs, and run workflows. Tokens are injected by the gateway, never by the agent.
OneCLI connects AI agents to GitHub so they can read and write code, open pull requests, manage issues, and trigger workflows. The gateway injects GitHub credentials into API requests automatically.OneCLI supports two ways to connect GitHub:
An agent calling the GitHub API through the gateway, with no token management needed:
# List your repositoriescurl -s "https://api.github.com/user/repos?per_page=5&sort=updated" | jq '.[].full_name'# Create an issuecurl -s -X POST "https://api.github.com/repos/myorg/myrepo/issues" \ -H "Content-Type: application/json" \ -d '{"title": "Bug: login page timeout", "body": "The login page times out after 30s on slow connections."}'# Open a pull requestcurl -s -X POST "https://api.github.com/repos/myorg/myrepo/pulls" \ -H "Content-Type: application/json" \ -d '{"title": "Fix login timeout", "head": "fix/login-timeout", "base": "main"}'# Trigger a workflowcurl -s -X POST "https://api.github.com/repos/myorg/myrepo/actions/workflows/deploy.yml/dispatches" \ -H "Content-Type: application/json" \ -d '{"ref": "main"}'
The agent makes standard GitHub API calls. The gateway injects the right authentication header automatically: Bearer token for API calls, Basic auth for git-over-HTTPS.
Skip this section on OneCLI Cloud. It’s only for self-hosted OneCLI without GITHUB_CLIENT_ID and GITHUB_CLIENT_SECRET set, or if you want your own company name on GitHub’s consent screen. For the GitHub App, see GitHub App self-hosted.
1. Create the OAuth app
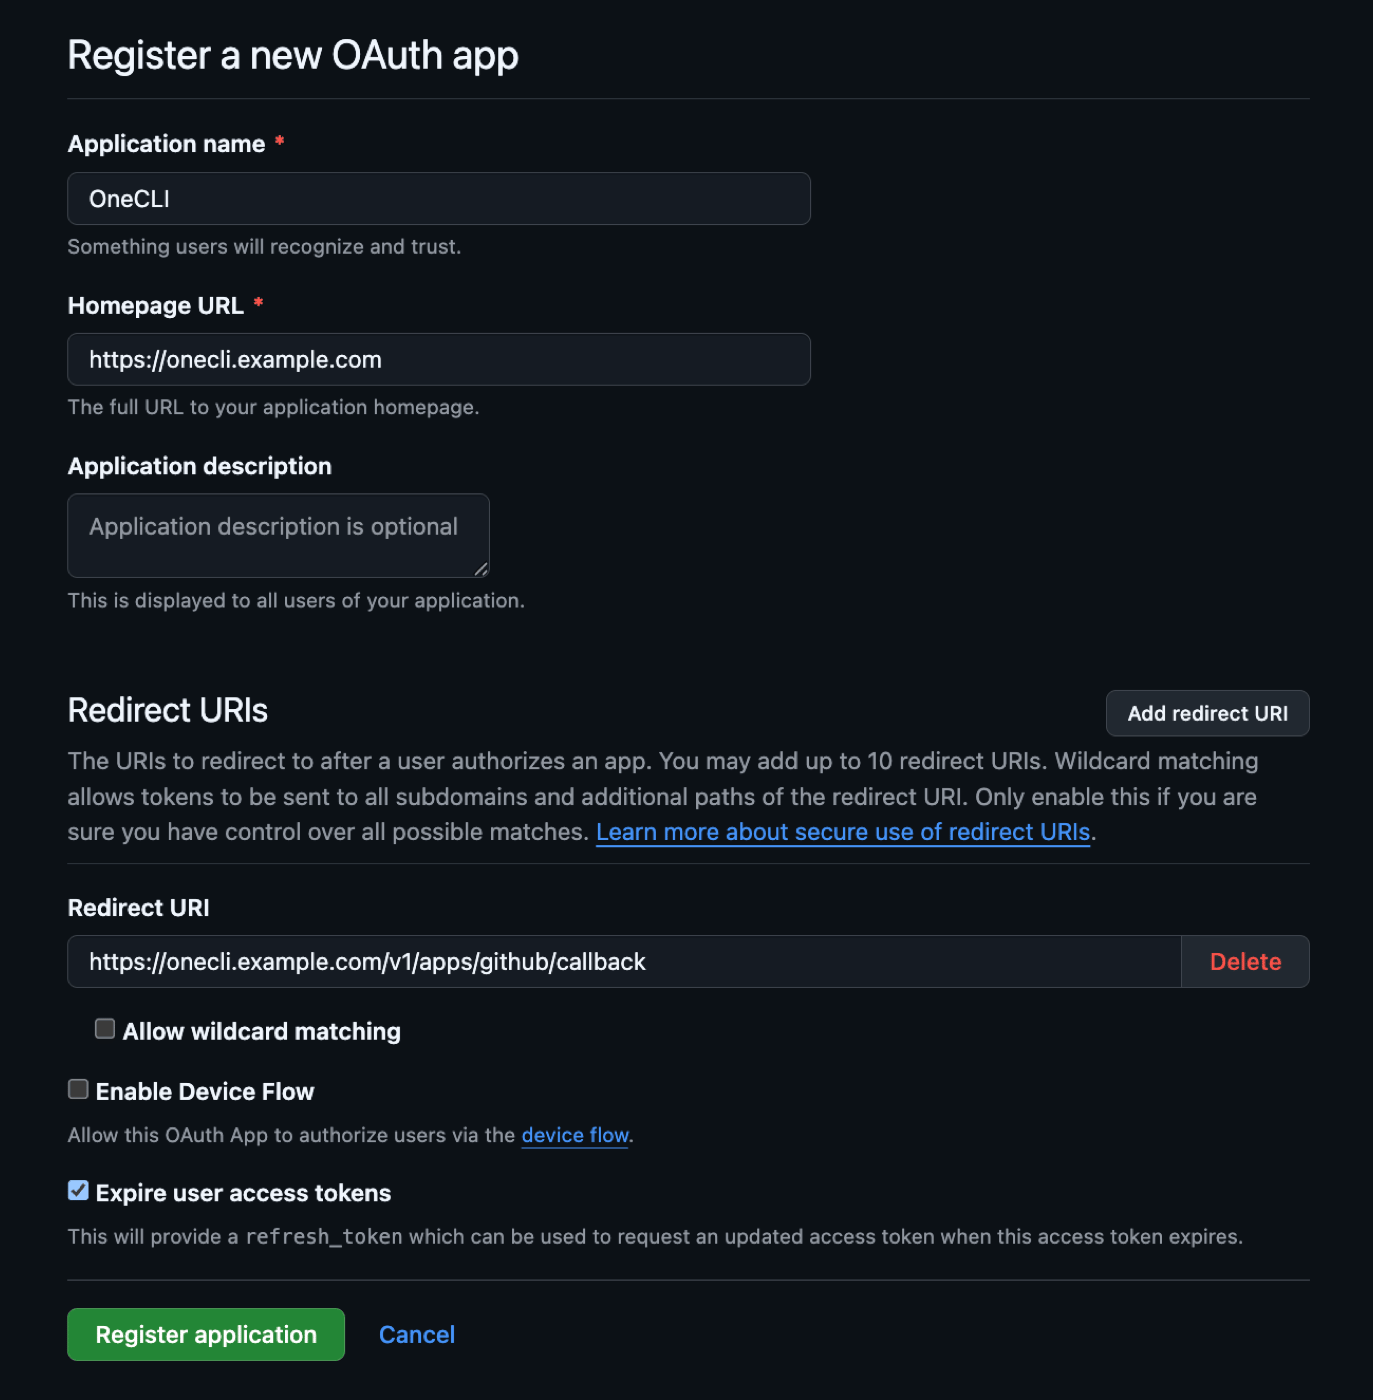
In GitHub, open Settings > Developer settings > OAuth Apps > New OAuth App (use your organization’s settings to own it there). Name it OneCLI and enter your homepage URL.
The new OAuth app form, filled in.
2. Add the callback URL
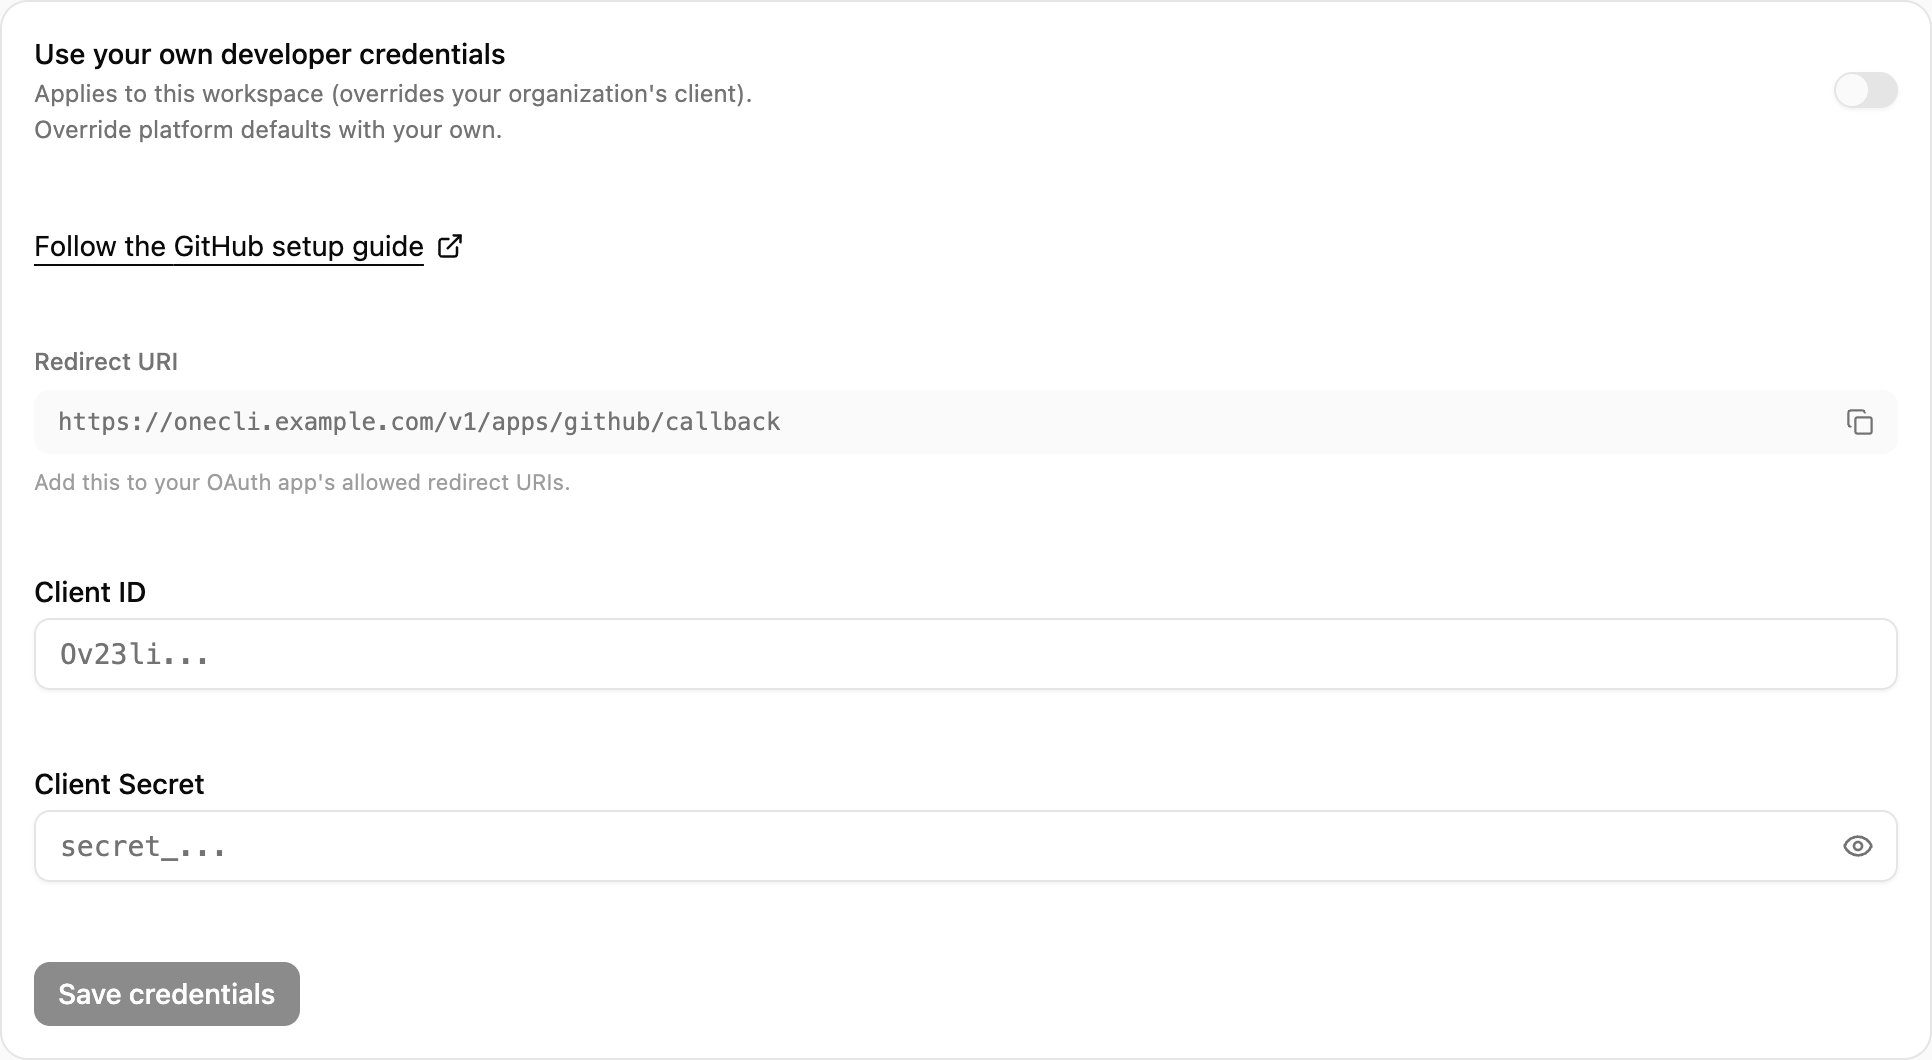
In OneCLI, open Connections > GitHub > Custom credentials and copy the Redirect URI. In GitHub, paste it into Redirect URI and select Register application. GitHub OAuth apps don’t take scopes here: OneCLI requests repo, user, gist, notifications, project, codespace, and workflow when you connect.
Copy the Redirect URI from Custom credentials in OneCLI.
3. Connect with your app
Copy the Client ID, then select Generate a new client secret and copy it. Paste both into Connections > GitHub > Custom credentials, select Save & Connect, and authorize in GitHub.
For teams and organizations. A GitHub App gives you repo-level access control and organizational visibility. Org admins can see which repos are connected and approve or revoke access at any time.
Open the OneCLI dashboard and navigate to Connections > GitHub App.
2
Configure credentials (self-hosted only)
If you’re using OneCLI Cloud, skip this step. Platform credentials are pre-configured.For self-hosted deployments, create a GitHub App and enter your App ID, App Slug, and Private Key.
3
Install the app
Click Connect GitHub App. You’ll be redirected to GitHub where you can:
Select the organization or personal account
Choose All repositories or Only select repositories
Once connected, the dashboard shows a permissions panel where you control what agents can do with GitHub. Each action has three modes: Allow (green), Ask (yellow, requires human approval), and Block (red, request is rejected).Read-only actions:
Action
Description
List repositories
Browse repos the account can access
Read repository
Read code, commits, branches
List issues
View issues on a repo
List pull requests
View open/closed PRs
Write / delete actions:
Action
Description
Create issue
Open new issues
Create pull request
Open PRs against a repo
Create comment
Comment on issues and PRs
Delete / close
Close issues, delete branches
Use the Read-only preset to allow all read actions and block writes, or switch to Custom to configure each action individually.
Both connection methods are per agent: grant the connection to each agent that needs it, choosing per tool what runs freely, what needs human approval, and what stays blocked — a read-only agent is a single grant. Organization rules add guardrails on top:
Rate limit API calls to stay within GitHub’s rate limits
Require manual approval for destructive operations (e.g., deleting branches)
Scope a connection to specific repositories with a session policy
Everything is checked before credential injection, so a blocked request never touches your GitHub token.
How do I keep my GitHub token out of the agent's context?
Don’t set GITHUB_TOKEN or store a token in the agent’s git config. Connect GitHub in OneCLI, and the gateway adds Bearer auth for API calls and Basic auth for git-over-HTTPS at the proxy. See How it works.
OAuth or GitHub App?
OAuth reaches every repo you can access and suits personal use. A GitHub App reaches only selected repos and suits teams. See Comparison.
How do I reconnect or replace the GitHub credential?
Reconnect from Connections > GitHub in the dashboard. Agents with access use the new credential automatically.
Can I require approval before an agent merges or pushes?
{"docsConfig":{"theme":"mint","$schema":"https://mintlify.com/docs.json","name":"OneCLI","colors":{"primary":"#19BA5D","light":"#34D474","dark":"#128A45"},"logo":{"light":"https://mintcdn.com/chartdbinc/3IvBQeNyWpN0X2ob/logo/logo-full-light.svg?fit=max\u0026auto=format\u0026n=3IvBQeNyWpN0X2ob\u0026q=85\u0026s=630ee6bb5c7441548135c690b3e18d35","dark":"https://mintcdn.com/chartdbinc/3IvBQeNyWpN0X2ob/logo/logo-full-dark.svg?fit=max\u0026auto=format\u0026n=3IvBQeNyWpN0X2ob\u0026q=85\u0026s=c80db357e121f4676dba423c01304258","href":"/"},"favicon":"https://mintcdn.com/chartdbinc/wh8636A1-I7XVdgP/favicon.png?fit=max\u0026auto=format\u0026n=wh8636A1-I7XVdgP\u0026q=85\u0026s=71b6d9b7afc7659e690354e389db9da8","appearance":{"default":"light"},"background":{"color":{"light":"#FAFAF9","dark":"#1A1918"}},"navbar":{"links":[{"href":"https://github.com/onecli/onecli","label":"GitHub"},{"href":"https://onecli.sh","label":"Install"}]},"footer":{"socials":{"github":"https://github.com/onecli"}},"fonts":{"heading":{"family":"Overused Grotesk","weight":600,"source":"fonts/OverusedGroteskRoman-VF.woff2","format":"woff2"}},"contextual":{"options":["copy","view","chatgpt","claude","perplexity","mcp","cursor","vscode"],"display":"header"},"styling":{"latex":false},"navigation":{"global":{"anchors":[{"anchor":"GitHub","icon":"https://mintlify.s3.us-west-1.amazonaws.com/chartdbinc/images/github.svg","href":"https://github.com/onecli"}]},"pages":[]}},"deployment":{"deploymentMetadataValue":{"subdomain":"chartdbinc","hasAudioNarration":false,"actualSubdomain":"chartdbinc","customDomains":["onecli.sh"],"gitSource":{"type":"github","owner":"onecli","repo":"onecli-docs","deployBranch":"main","contentDirectory":"","isPrivate":true,"mountPath":"","label":""},"entitlements":{},"buildId":"6aed6ecd1adb743cd28e52b5","clientVersion":"0.0.4087","searchFilterCounts":[{"language":"default","tag":"API Reference","count":240},{"language":"default","tag":"Workspace","count":105},{"language":"default","tag":"Integrations","count":88},{"language":"default","tag":"All app connections","count":64},{"language":"default","tag":"Enterprise","count":57},{"language":"default","tag":"Organization","count":52},{"language":"default","tag":"Apps","count":29},{"language":"default","tag":"Channels","count":28},{"language":"default","tag":"Platform","count":21},{"language":"default","tag":"Guides","count":17}]},"assistantConfig":{"enableAskAiButton":false,"enableStarterQuestions":false,"enableAskAiSearchBar":true},"basePath":"/docs","hasChatPermissions":false,"hasWebMcpPermissions":false,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"rbac-expansion","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"full-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-sso-scim","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-signup","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-dual-write","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-enabled","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"approve-review-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-metadata","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"sso-setup-deadline-banner","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-serve","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"live-agents","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"comment-mode","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"googleFontsInlined":false},"customCss":[{"filePath":"style.css","content":"a.nav-anchor div.mr-4.rounded-md{--tw-ring-color: transparent !important;--tw-ring-shadow: 0 0 0 0 transparent !important;--tw-ring-offset-shadow: 0 0 0 0 transparent !important;box-shadow:none!important;background:transparent!important;filter:none!important;transition:opacity 0.15s ease!important}a.nav-anchor:hover div.mr-4.rounded-md{--tw-ring-color: transparent !important;--tw-ring-shadow: 0 0 0 0 transparent !important;--tw-ring-offset-shadow: 0 0 0 0 transparent !important;box-shadow:none!important;background:transparent!important;filter:none!important;opacity:0.7!important}a.nav-anchor div.mr-4.rounded-md img{opacity:1!important;filter:none!important;background:transparent!important}a.nav-anchor:hover div.mr-4.rounded-md img{opacity:1!important;filter:none!important;background:transparent!important}.dark a.nav-anchor div.mr-4.rounded-md img,[data-theme=\"dark\"] a.nav-anchor div.mr-4.rounded-md img{filter:invert(1)!important}"}],"page":{"pagePath":"integrations/github","slug":"/integrations/github","pageMetadata":{"title":"Let AI Agents Open PRs and Issues on GitHub","sidebarTitle":"GitHub","description":"Connect GitHub with OAuth or a GitHub App so agents can push code, open PRs, and run workflows. Tokens are injected by the gateway, never by the agent.","canonical":"https://onecli.sh/docs/integrations/github","href":"/integrations/github"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"Connect GitHub with OAuth or a GitHub App so agents can push code, open PRs, and run workflows. Tokens are injected by the gateway, never by the agent.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,code:`code`,li:`li`,ol:`ol`,p:`p`,pre:`pre`,span:`span`,strong:`strong`,tbody:`tbody`,td:`td`,th:`th`,thead:`thead`,tr:`tr`,ul:`ul`,..._provideComponents(),...props.components},{Accordion,AccordionGroup,CodeBlock,Frame,Heading,Info,OptimizedImage,Step,Steps,Table}=_components;if(!Accordion)_missingMdxReference(`Accordion`,true);if(!AccordionGroup)_missingMdxReference(`AccordionGroup`,true);if(!CodeBlock)_missingMdxReference(`CodeBlock`,true);if(!Frame)_missingMdxReference(`Frame`,true);if(!Heading)_missingMdxReference(`Heading`,true);if(!Info)_missingMdxReference(`Info`,true);if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);if(!Step)_missingMdxReference(`Step`,true);if(!Steps)_missingMdxReference(`Steps`,true);if(!Table)_missingMdxReference(`Table`,true);return _jsxs(_Fragment,{children:[_jsx(Heading,{level:`2`,id:`overview`,children:`Overview`}),`\n`,_jsx(_components.p,{children:`OneCLI connects AI agents to GitHub so they can read and write code, open pull requests, manage issues, and trigger workflows. The gateway injects GitHub credentials into API requests automatically.`}),`\n`,_jsx(_components.p,{children:`OneCLI supports two ways to connect GitHub:`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Method`}),_jsx(_components.th,{children:`Access scope`}),_jsx(_components.th,{children:`Best for`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`OAuth`})}),_jsx(_components.td,{children:`All repos the user can access`}),_jsx(_components.td,{children:`Personal use, quick setup`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`GitHub App`})}),_jsx(_components.td,{children:`Only selected repos`}),_jsx(_components.td,{children:`Teams, organizations`})]})]})]}),`\n`,_jsx(Heading,{level:`2`,id:`what-you-will-set-up`,children:`What you will set up`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`A GitHub connection through OAuth or a GitHub App`}),`\n`,_jsx(_components.li,{children:`Token injection on API calls and git-over-HTTPS`}),`\n`,_jsx(_components.li,{children:`Per-action allow, ask, or block controls for each agent`}),`\n`]}),`\n`,_jsx(Heading,{level:`2`,id:`quick-example`,children:`Quick example`}),`\n`,_jsx(_components.p,{children:`An agent calling the GitHub API through the gateway, with no token management needed:`}),`\n`,_jsx(CodeBlock,{filename:``,numberOfLines:`17`,language:`shellscript`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`shellscript`,children:_jsxs(_components.code,{language:`shellscript`,numberOfLines:`17`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# List your repositories`})}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`curl`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -s`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` \"https://api.github.com/user/repos?per_page=5\u0026sort=updated\"`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:` |`}),_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:` jq`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` '.[].full_name'`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# Create an issue`})}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`curl`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -s`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -X`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` POST`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` \"https://api.github.com/repos/myorg/myrepo/issues\"`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D7BA7D`},children:` \\\\`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -H`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` \"Content-Type: application/json\"`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D7BA7D`},children:` \\\\`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -d`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` '{\"title\": \"Bug: login page timeout\", \"body\": \"The login page times out after 30s on slow connections.\"}'`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# Open a pull request`})}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`curl`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -s`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -X`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` POST`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` \"https://api.github.com/repos/myorg/myrepo/pulls\"`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D7BA7D`},children:` \\\\`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -H`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` \"Content-Type: application/json\"`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D7BA7D`},children:` \\\\`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -d`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` '{\"title\": \"Fix login timeout\", \"head\": \"fix/login-timeout\", \"base\": \"main\"}'`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# Trigger a workflow`})}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`curl`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -s`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -X`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` POST`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` \"https://api.github.com/repos/myorg/myrepo/actions/workflows/deploy.yml/dispatches\"`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D7BA7D`},children:` \\\\`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -H`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` \"Content-Type: application/json\"`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D7BA7D`},children:` \\\\`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -d`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` '{\"ref\": \"main\"}'`})]}),`\n`]})})}),`\n`,_jsxs(_components.p,{children:[`The agent makes standard GitHub API calls. The gateway injects the right authentication header automatically: `,_jsx(_components.code,{children:`Bearer`}),` token for API calls, Basic auth for git-over-HTTPS.`]}),`\n`,_jsx(Heading,{level:`2`,id:`oauth`,children:`OAuth`}),`\n`,_jsx(_components.p,{children:`Connect your personal GitHub account. The agent gets access to all repositories you can see.`}),`\n`,_jsx(Heading,{level:`3`,id:`setup`,children:`Setup`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Go to Connections`,children:_jsxs(_components.p,{children:[`Open the OneCLI dashboard and navigate to `,_jsx(_components.strong,{children:`Connections`}),` > `,_jsx(_components.strong,{children:`GitHub`}),`.`]})}),_jsxs(Step,{title:`Authorize`,children:[_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Connect GitHub`}),`. You’ll be redirected to GitHub to authorize OneCLI. Review the permissions and click `,_jsx(_components.strong,{children:`Authorize`}),`.`]}),_jsx(Frame,{caption:`The GitHub connect window on OneCLI Cloud.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-connect-github.png?fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=522defecbaca128616a8355110cbc263`,alt:`OneCLI connect window for GitHub on Cloud, showing the Connect to GitHub button.`,\"data-og-width\":`1056`,width:`1056`,\"data-og-height\":`1078`,height:`1078`,\"data-path\":`images/integrations/github/onecli-connect-github.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-connect-github.png?w=280\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=9b9e3f175dbcaf3291b53965bd8349d9 280w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-connect-github.png?w=560\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=b38b90a7389aeb61dac2c96daf1da9b0 560w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-connect-github.png?w=840\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=d7fc5bdc906af40a80ba11fbbaea2a45 840w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-connect-github.png?w=1100\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=3328df50589609cfc8df9df0c58389d8 1100w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-connect-github.png?w=1650\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=8c8f554e469f71512722f1ac65a177b0 1650w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-connect-github.png?w=2500\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=363e33277301fa5f9eba138e2ff8dc40 2500w`})})]})]}),`\n`,_jsx(`a`,{id:`self-hosted`,style:{scrollMarginTop:`8rem`}}),`\n`,_jsx(Heading,{level:`3`,id:`self-hosted-use-your-own-github-oauth-app`,children:`Self-hosted: use your own GitHub OAuth app`}),`\n`,_jsx(Info,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Skip this section on OneCLI Cloud.`}),` It’s only for self-hosted OneCLI without `,_jsx(_components.code,{children:`GITHUB_CLIENT_ID`}),` and `,_jsx(_components.code,{children:`GITHUB_CLIENT_SECRET`}),` set, or if you want your own company name on GitHub’s consent screen. For the GitHub App, see `,_jsx(_components.a,{href:`/integrations/github-app#self-hosted`,children:`GitHub App self-hosted`}),`.`]})}),`\n`,_jsxs(AccordionGroup,{children:[_jsxs(Accordion,{title:`1. Create the OAuth app`,defaultOpen:true,id:`1-create-the-oauth-app`,children:[_jsxs(_components.p,{children:[`In GitHub, open `,_jsx(_components.strong,{children:`Settings`}),` > `,_jsx(_components.strong,{children:`Developer settings`}),` > `,_jsx(_components.strong,{children:`OAuth Apps`}),` > `,_jsx(_components.strong,{children:`New OAuth App`}),` (use your organization’s settings to own it there). Name it `,_jsx(_components.code,{children:`OneCLI`}),` and enter your homepage URL.`]}),_jsx(Frame,{caption:`The new OAuth app form, filled in.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/chartdbinc/a0Jq8zKs4ya-oJiN/images/integrations/github/01-new-oauth-app.png?fit=max\u0026auto=format\u0026n=a0Jq8zKs4ya-oJiN\u0026q=85\u0026s=3fe70128bf2ed5bbc712296d227a72c5`,alt:`GitHub Register a new OAuth app form with the name OneCLI, a homepage URL, and the OneCLI callback in the Redirect URI field.`,\"data-og-width\":`1373`,width:`1373`,\"data-og-height\":`1400`,height:`1400`,\"data-path\":`images/integrations/github/01-new-oauth-app.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/chartdbinc/a0Jq8zKs4ya-oJiN/images/integrations/github/01-new-oauth-app.png?w=280\u0026fit=max\u0026auto=format\u0026n=a0Jq8zKs4ya-oJiN\u0026q=85\u0026s=72c40f0b8cd47747be230133c96d34d0 280w, https://mintcdn.com/chartdbinc/a0Jq8zKs4ya-oJiN/images/integrations/github/01-new-oauth-app.png?w=560\u0026fit=max\u0026auto=format\u0026n=a0Jq8zKs4ya-oJiN\u0026q=85\u0026s=39b03bb5a91155feec7594f84d819374 560w, https://mintcdn.com/chartdbinc/a0Jq8zKs4ya-oJiN/images/integrations/github/01-new-oauth-app.png?w=840\u0026fit=max\u0026auto=format\u0026n=a0Jq8zKs4ya-oJiN\u0026q=85\u0026s=5da2b5c5d9af470dac5404f6178fcd6b 840w, https://mintcdn.com/chartdbinc/a0Jq8zKs4ya-oJiN/images/integrations/github/01-new-oauth-app.png?w=1100\u0026fit=max\u0026auto=format\u0026n=a0Jq8zKs4ya-oJiN\u0026q=85\u0026s=84e6a166d895c03a0b93c429f673ab05 1100w, https://mintcdn.com/chartdbinc/a0Jq8zKs4ya-oJiN/images/integrations/github/01-new-oauth-app.png?w=1650\u0026fit=max\u0026auto=format\u0026n=a0Jq8zKs4ya-oJiN\u0026q=85\u0026s=af3d2cf7a2d639684a04fb562b6bdc28 1650w, https://mintcdn.com/chartdbinc/a0Jq8zKs4ya-oJiN/images/integrations/github/01-new-oauth-app.png?w=2500\u0026fit=max\u0026auto=format\u0026n=a0Jq8zKs4ya-oJiN\u0026q=85\u0026s=06437fd40f0198697453c9f284c98df2 2500w`})})]}),_jsxs(Accordion,{title:`2. Add the callback URL`,id:`2-add-the-callback-url`,children:[_jsxs(_components.p,{children:[`In OneCLI, open `,_jsx(_components.strong,{children:`Connections`}),` > `,_jsx(_components.strong,{children:`GitHub`}),` > `,_jsx(_components.strong,{children:`Custom credentials`}),` and copy the `,_jsx(_components.strong,{children:`Redirect URI`}),`. In GitHub, paste it into `,_jsx(_components.strong,{children:`Redirect URI`}),` and select `,_jsx(_components.strong,{children:`Register application`}),`. GitHub OAuth apps don’t take scopes here: OneCLI requests `,_jsx(_components.code,{children:`repo`}),`, `,_jsx(_components.code,{children:`user`}),`, `,_jsx(_components.code,{children:`gist`}),`, `,_jsx(_components.code,{children:`notifications`}),`, `,_jsx(_components.code,{children:`project`}),`, `,_jsx(_components.code,{children:`codespace`}),`, and `,_jsx(_components.code,{children:`workflow`}),` when you connect.`]}),_jsx(Frame,{caption:`Copy the Redirect URI from Custom credentials in OneCLI.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-custom-credentials-github.png?fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=d0805f984faadad1503c94d4f1cdc4d0`,alt:`OneCLI Custom credentials card for GitHub with the setup guide link, the Redirect URI and its copy button, and the client ID and secret fields.`,\"data-og-width\":`1932`,width:`1932`,\"data-og-height\":`1060`,height:`1060`,\"data-path\":`images/integrations/github/onecli-custom-credentials-github.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-custom-credentials-github.png?w=280\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=79d0e5d3f26d5190ce22d0c103df46d4 280w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-custom-credentials-github.png?w=560\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=937352b62ff03b28f9c352f6a33bd3e9 560w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-custom-credentials-github.png?w=840\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=dcf253d46b9394ff5f0cbbe864b35cad 840w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-custom-credentials-github.png?w=1100\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=67b4512e152b5a423f2d6f62e0a10005 1100w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-custom-credentials-github.png?w=1650\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=38eaecc326ffd239f53f02175c30cc46 1650w, https://mintcdn.com/chartdbinc/L4k9tYUENUtEpMY8/images/integrations/github/onecli-custom-credentials-github.png?w=2500\u0026fit=max\u0026auto=format\u0026n=L4k9tYUENUtEpMY8\u0026q=85\u0026s=ad2fa9e3d4016485951b7feb8f7e1a36 2500w`})})]}),_jsx(Accordion,{title:`3. Connect with your app`,id:`3-connect-with-your-app`,children:_jsxs(_components.p,{children:[`Copy the `,_jsx(_components.strong,{children:`Client ID`}),`, then select `,_jsx(_components.strong,{children:`Generate a new client secret`}),` and copy it. Paste both into `,_jsx(_components.strong,{children:`Connections`}),` > `,_jsx(_components.strong,{children:`GitHub`}),` > `,_jsx(_components.strong,{children:`Custom credentials`}),`, select `,_jsx(_components.strong,{children:`Save \u0026 Connect`}),`, and authorize in GitHub.`]})})]}),`\n`,_jsx(Heading,{level:`3`,id:`permissions`,children:`Permissions`}),`\n`,_jsx(_components.p,{children:`The OAuth connection requests these scopes:`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Scope`}),_jsx(_components.th,{children:`Name`}),_jsx(_components.th,{children:`Access`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`repo`})}),_jsx(_components.td,{children:`Repositories`}),_jsx(_components.td,{children:`Read \u0026 write (code, issues, PRs)`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`user`})}),_jsx(_components.td,{children:`Profile`}),_jsx(_components.td,{children:`Read (email, name, avatar)`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`gist`})}),_jsx(_components.td,{children:`Gists`}),_jsx(_components.td,{children:`Read \u0026 write`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`notifications`})}),_jsx(_components.td,{children:`Notifications`}),_jsx(_components.td,{children:`Read`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`project`})}),_jsx(_components.td,{children:`Projects`}),_jsx(_components.td,{children:`Read \u0026 write`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`codespace`})}),_jsx(_components.td,{children:`Codespaces`}),_jsx(_components.td,{children:`Read \u0026 write`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`workflow`})}),_jsx(_components.td,{children:`Actions`}),_jsx(_components.td,{children:`Read \u0026 write (workflow files)`})]})]})]}),`\n`,_jsx(AccordionGroup,{children:_jsxs(Accordion,{title:`More about OAuth: how it works, use cases, limitations`,id:`more-about-oauth-how-it-works-use-cases-limitations`,children:[_jsx(_components.p,{children:_jsx(_components.strong,{children:`How it works`})}),_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`You authorize OneCLI via GitHub’s OAuth flow`}),`\n`,_jsx(_components.li,{children:`OneCLI receives a long-lived access token and encrypts it`}),`\n`,_jsxs(_components.li,{children:[`When an agent sends a request to `,_jsx(_components.code,{children:`api.github.com`}),`, the gateway injects the token as a `,_jsx(_components.code,{children:`Bearer`}),` header`]}),`\n`,_jsxs(_components.li,{children:[`For git operations over HTTPS (`,_jsx(_components.code,{children:`github.com`}),`), the gateway injects Basic auth credentials`]}),`\n`]}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`Use cases`})}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Coding agents creating branches, committing code, and opening pull requests`}),`\n`,_jsx(_components.li,{children:`Agents reviewing PRs and leaving comments`}),`\n`,_jsx(_components.li,{children:`Triggering GitHub Actions workflows from an agent`}),`\n`,_jsx(_components.li,{children:`Reading repository contents during code generation`}),`\n`]}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`Limitations`})}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`The token has access to all repositories you can see, not just selected ones`}),`\n`,_jsx(_components.li,{children:`No organizational visibility or approval flow`}),`\n`,_jsx(_components.li,{children:`Token is long-lived until you revoke the connection`}),`\n`]})]})}),`\n`,_jsx(Heading,{level:`2`,id:`github-app`,children:`GitHub App`}),`\n`,_jsx(_components.p,{children:`For teams and organizations. A GitHub App gives you repo-level access control and organizational visibility. Org admins can see which repos are connected and approve or revoke access at any time.`}),`\n`,_jsx(Heading,{level:`3`,id:`setup-2`,children:`Setup`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Go to Connections`,children:_jsxs(_components.p,{children:[`Open the OneCLI dashboard and navigate to `,_jsx(_components.strong,{children:`Connections`}),` > `,_jsx(_components.strong,{children:`GitHub App`}),`.`]})}),_jsxs(Step,{title:`Configure credentials (self-hosted only)`,children:[_jsx(_components.p,{children:`If you’re using OneCLI Cloud, skip this step. Platform credentials are pre-configured.`}),_jsxs(_components.p,{children:[`For self-hosted deployments, `,_jsx(_components.a,{href:`https://docs.github.com/en/apps/creating-github-apps/registering-a-github-app/registering-a-github-app`,children:`create a GitHub App`}),` and enter your `,_jsx(_components.strong,{children:`App ID`}),`, `,_jsx(_components.strong,{children:`App Slug`}),`, and `,_jsx(_components.strong,{children:`Private Key`}),`.`]})]}),_jsxs(Step,{title:`Install the app`,children:[_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Connect GitHub App`}),`. You’ll be redirected to GitHub where you can:`]}),_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`Select the organization or personal account`}),`\n`,_jsxs(_components.li,{children:[`Choose `,_jsx(_components.strong,{children:`All repositories`}),` or `,_jsx(_components.strong,{children:`Only select repositories`})]}),`\n`,_jsx(_components.li,{children:`Review the permissions`}),`\n`]}),_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Install`}),` to complete the connection.`]})]})]}),`\n`,_jsx(Heading,{level:`3`,id:`permissions-2`,children:`Permissions`}),`\n`,_jsx(_components.p,{children:`The GitHub App requests only the permissions your agents need:`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Permission`}),_jsx(_components.th,{children:`Access`}),_jsx(_components.th,{children:`Description`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Contents`}),_jsx(_components.td,{children:`Read \u0026 write`}),_jsx(_components.td,{children:`Code, commits, and branches`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Pull requests`}),_jsx(_components.td,{children:`Read \u0026 write`}),_jsx(_components.td,{children:`Create, review, and merge PRs`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Issues`}),_jsx(_components.td,{children:`Read \u0026 write`}),_jsx(_components.td,{children:`Create and manage issues`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Actions`}),_jsx(_components.td,{children:`Read \u0026 write`}),_jsx(_components.td,{children:`View runs and trigger workflows`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Checks`}),_jsx(_components.td,{children:`Read \u0026 write`}),_jsx(_components.td,{children:`Read CI results, create check runs`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Commit statuses`}),_jsx(_components.td,{children:`Read \u0026 write`}),_jsx(_components.td,{children:`Read and set status checks`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Discussions`}),_jsx(_components.td,{children:`Read \u0026 write`}),_jsx(_components.td,{children:`Read and participate in discussions`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Projects`}),_jsx(_components.td,{children:`Read \u0026 write`}),_jsx(_components.td,{children:`Manage project boards`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Metadata`}),_jsx(_components.td,{children:`Read-only`}),_jsx(_components.td,{children:`Repository metadata (always granted)`})]})]})]}),`\n`,_jsx(AccordionGroup,{children:_jsxs(Accordion,{title:`More about the GitHub App: how it works, use cases`,id:`more-about-the-github-app-how-it-works-use-cases`,children:[_jsx(_components.p,{children:_jsx(_components.strong,{children:`How it works`})}),_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`You install the GitHub App on your organization or account and select which repositories it can access`}),`\n`,_jsx(_components.li,{children:`OneCLI receives the app’s private key and installation ID`}),`\n`,_jsx(_components.li,{children:`The gateway signs a short-lived JWT and exchanges it for an installation access token (1hr TTL)`}),`\n`,_jsx(_components.li,{children:`The token is injected into API requests and automatically refreshed when it expires`}),`\n`]}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`Use cases`})}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Organizations giving agents access to specific repos without exposing the full account`}),`\n`,_jsx(_components.li,{children:`Teams where admins need visibility into which repos agents can access`}),`\n`,_jsx(_components.li,{children:`Production deployments where token rotation should be automatic`}),`\n`,_jsx(_components.li,{children:`Compliance environments where long-lived tokens are not acceptable`}),`\n`]})]})}),`\n`,_jsx(Heading,{level:`3`,id:`managing-access`,children:`Managing access`}),`\n`,_jsx(_components.p,{children:`After connecting, you can change which repositories the app can access:`}),`\n`,_jsxs(_components.ol,{children:[`\n`,_jsxs(_components.li,{children:[`Go to `,_jsx(_components.strong,{children:`Connections`}),` > `,_jsx(_components.strong,{children:`GitHub App`}),` in the OneCLI dashboard`]}),`\n`,_jsxs(_components.li,{children:[`Click `,_jsx(_components.strong,{children:`Manage`}),` on the connection`]}),`\n`,_jsx(_components.li,{children:`You’ll be taken to GitHub’s installation settings where you can add or remove repositories`}),`\n`]}),`\n`,_jsx(Heading,{level:`2`,id:`comparison`,children:`Comparison`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{}),_jsx(_components.th,{children:`OAuth`}),_jsx(_components.th,{children:`GitHub App`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Repo access`})}),_jsx(_components.td,{children:`All repos the user can see`}),_jsx(_components.td,{children:`Only selected repos`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Token lifetime`})}),_jsx(_components.td,{children:`Long-lived`}),_jsx(_components.td,{children:`1 hour (auto-refreshed)`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Org visibility`})}),_jsx(_components.td,{children:`Not visible to admins`}),_jsx(_components.td,{children:`Visible to org admins`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Org approval`})}),_jsx(_components.td,{children:`Not required`}),_jsx(_components.td,{children:`Required`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Setup`})}),_jsx(_components.td,{children:`One-click OAuth`}),_jsx(_components.td,{children:`Install app + select repos`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Best for`})}),_jsx(_components.td,{children:`Personal, quick start`}),_jsx(_components.td,{children:`Teams, production`})]})]})]}),`\n`,_jsx(Heading,{level:`2`,id:`per-action-permissions`,children:`Per-action permissions`}),`\n`,_jsxs(_components.p,{children:[`Once connected, the dashboard shows a permissions panel where you control what agents can do with GitHub. Each action has three modes: `,_jsx(_components.strong,{children:`Allow`}),` (green), `,_jsx(_components.strong,{children:`Ask`}),` (yellow, requires human approval), and `,_jsx(_components.strong,{children:`Block`}),` (red, request is rejected).`]}),`\n`,_jsx(_components.p,{children:_jsx(_components.strong,{children:`Read-only actions:`})}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Action`}),_jsx(_components.th,{children:`Description`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`List repositories`}),_jsx(_components.td,{children:`Browse repos the account can access`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Read repository`}),_jsx(_components.td,{children:`Read code, commits, branches`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`List issues`}),_jsx(_components.td,{children:`View issues on a repo`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`List pull requests`}),_jsx(_components.td,{children:`View open/closed PRs`})]})]})]}),`\n`,_jsx(_components.p,{children:_jsx(_components.strong,{children:`Write / delete actions:`})}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Action`}),_jsx(_components.th,{children:`Description`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Create issue`}),_jsx(_components.td,{children:`Open new issues`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Create pull request`}),_jsx(_components.td,{children:`Open PRs against a repo`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Create comment`}),_jsx(_components.td,{children:`Comment on issues and PRs`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Delete / close`}),_jsx(_components.td,{children:`Close issues, delete branches`})]})]})]}),`\n`,_jsxs(_components.p,{children:[`Use the `,_jsx(_components.strong,{children:`Read-only`}),` preset to allow all read actions and block writes, or switch to `,_jsx(_components.strong,{children:`Custom`}),` to configure each action individually.`]}),`\n`,_jsx(Heading,{level:`2`,id:`controlling-access`,children:`Controlling access`}),`\n`,_jsxs(_components.p,{children:[`Both connection methods are per agent: `,_jsx(_components.a,{href:`/guides/agent-access`,children:`grant`}),` the connection to each agent that needs it, choosing per tool what runs freely, what needs human approval, and what stays blocked — a read-only agent is a single grant. Organization `,_jsx(_components.a,{href:`/guides/rules`,children:`rules`}),` add guardrails on top:`]}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Rate limit API calls to stay within GitHub’s rate limits`}),`\n`,_jsx(_components.li,{children:`Require manual approval for destructive operations (e.g., deleting branches)`}),`\n`,_jsx(_components.li,{children:`Scope a connection to specific repositories with a session policy`}),`\n`]}),`\n`,_jsx(_components.p,{children:`Everything is checked before credential injection, so a blocked request never touches your GitHub token.`}),`\n`,_jsx(Heading,{level:`2`,id:`faq`,children:`FAQ`}),`\n`,_jsxs(AccordionGroup,{children:[_jsx(Accordion,{title:`How do I keep my GitHub token out of the agent's context?`,id:`how-do-i-keep-my-github-token-out-of-the-agents-context`,children:_jsxs(_components.p,{children:[`Don’t set `,_jsx(_components.code,{children:`GITHUB_TOKEN`}),` or store a token in the agent’s git config. Connect GitHub in OneCLI, and the gateway adds `,_jsx(_components.code,{children:`Bearer`}),` auth for API calls and Basic auth for git-over-HTTPS at the proxy. See `,_jsx(_components.a,{href:`/how-it-works`,children:`How it works`}),`.`]})}),_jsx(Accordion,{title:`OAuth or GitHub App?`,id:`oauth-or-github-app`,children:_jsxs(_components.p,{children:[`OAuth reaches every repo you can access and suits personal use. A GitHub App reaches only selected repos and suits teams. See `,_jsx(_components.a,{href:`#comparison`,children:`Comparison`}),`.`]})}),_jsx(Accordion,{title:`How do I reconnect or replace the GitHub credential?`,id:`how-do-i-reconnect-or-replace-the-github-credential`,children:_jsxs(_components.p,{children:[`Reconnect from `,_jsx(_components.strong,{children:`Connections`}),` > `,_jsx(_components.strong,{children:`GitHub`}),` in the dashboard. Agents with access use the new credential automatically.`]})}),_jsx(Accordion,{title:`Can I require approval before an agent merges or pushes?`,id:`can-i-require-approval-before-an-agent-merges-or-pushes`,children:_jsxs(_components.p,{children:[`Yes. Use `,_jsx(_components.a,{href:`#per-action-permissions`,children:`per-action permissions`}),` when you `,_jsx(_components.a,{href:`/guides/agent-access`,children:`grant`}),` the connection, and `,_jsx(_components.a,{href:`/guides/rules`,children:`rules`}),` for organization-wide guardrails.`]})})]})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"config":{},"pageMetadata":{"title":"Let AI Agents Open PRs and Issues on GitHub","sidebarTitle":"GitHub","description":"Connect GitHub with OAuth or a GitHub App so agents can push code, open PRs, and run workflows. Tokens are injected by the gateway, never by the agent.","canonical":"https://onecli.sh/docs/integrations/github","href":"/integrations/github"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[{"title":"Overview","slug":"overview","depth":2,"children":[]},{"title":"What you will set up","slug":"what-you-will-set-up","depth":2,"children":[]},{"title":"Quick example","slug":"quick-example","depth":2,"children":[]},{"title":"OAuth","slug":"oauth","depth":2,"children":[{"title":"Setup","slug":"setup","depth":3,"children":[]},{"title":"Self-hosted: use your own GitHub OAuth app","slug":"self-hosted-use-your-own-github-oauth-app","depth":3,"children":[]},{"title":"Permissions","slug":"permissions","depth":3,"children":[]}]},{"title":"GitHub App","slug":"github-app","depth":2,"children":[{"title":"Setup","slug":"setup-2","depth":3,"children":[]},{"title":"Permissions","slug":"permissions-2","depth":3,"children":[]},{"title":"Managing access","slug":"managing-access","depth":3,"children":[]}]},{"title":"Comparison","slug":"comparison","depth":2,"children":[]},{"title":"Per-action permissions","slug":"per-action-permissions","depth":2,"children":[]},{"title":"Controlling access","slug":"controlling-access","depth":2,"children":[]},{"title":"FAQ","slug":"faq","depth":2,"children":[]}],"codeExamples":{}},"jsLinks":["/docs/_mintlify/custom/chartdbinc/e8c5fc0faf4d8de9/infra/cloudfront/docs-response-headers.js"],"subdomain":"chartdbinc","siteName":"OneCLI","title":"Let AI Agents Open PRs and Issues on GitHub - OneCLI","navMaps":{"firstHrefInVersion":{},"firstHrefInLanguage":{}},"lastModified":"2026-11-03T01:51:11.664Z","originalFileLocation":"integrations/github.mdx"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"light\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"Connect GitHub with OAuth or a GitHub App so agents can push code, open PRs, and run workflows. Tokens are injected by the gateway, never by the agent.\">\u003cmeta data-mint-head name=\"application-name\" content=\"OneCLI\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"Let AI Agents Open PRs and Issues on GitHub - OneCLI\">\u003cmeta data-mint-head property=\"og:description\" content=\"Connect GitHub with OAuth or a GitHub App so agents can push code, open PRs, and run workflows. Tokens are injected by the gateway, never by the agent.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"OneCLI\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://onecli.sh/docs/integrations/github\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://chartdbinc.mintlify.site/docs/_mintlify/api/og/v2?division=Cloud+integrations\u0026amp;title=Let+AI+Agents+Open+PRs+and+Issues+on+GitHub\u0026amp;description=Connect+GitHub+with+OAuth+or+a+GitHub+App+so+agents+can+push+code%2C+open+PRs%2C+and+run+workflows.+Tokens+are+injected+by+the+gateway%2C+never+by+the+agent.\u0026amp;theme=4d31f9e8e68b774b9a2b22f5\u0026amp;signature=1fb4479217b8fea358c739378db2ca5c9bf11ff2f3f1c730a6f82f7e4af24075\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"Let AI Agents Open PRs and Issues on GitHub - OneCLI\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"Connect GitHub with OAuth or a GitHub App so agents can push code, open PRs, and run workflows. Tokens are injected by the gateway, never by the agent.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://chartdbinc.mintlify.site/docs/_mintlify/api/og/v2?division=Cloud+integrations\u0026amp;title=Let+AI+Agents+Open+PRs+and+Issues+on+GitHub\u0026amp;description=Connect+GitHub+with+OAuth+or+a+GitHub+App+so+agents+can+push+code%2C+open+PRs%2C+and+run+workflows.+Tokens+are+injected+by+the+gateway%2C+never+by+the+agent.\u0026amp;theme=4d31f9e8e68b774b9a2b22f5\u0026amp;signature=1fb4479217b8fea358c739378db2ca5c9bf11ff2f3f1c730a6f82f7e4af24075\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/docs/mintlify-assets/_mintlify/favicons/chartdbinc/M5-fw7HRdTdsqSgf/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"OneCLI\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#19BA5D\">\u003clink data-mint-head rel=\"canonical\" href=\"https://onecli.sh/docs/integrations/github\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/docs/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/docs/integrations/github.md\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://onecli.sh/#organization\",\"name\":\"OneCLI\",\"url\":\"https://onecli.sh\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/chartdbinc/3IvBQeNyWpN0X2ob/logo/logo-full-light.svg?fit=max\u0026auto=format\u0026n=3IvBQeNyWpN0X2ob\u0026q=85\u0026s=630ee6bb5c7441548135c690b3e18d35\"}},{\"@type\":\"WebSite\",\"@id\":\"https://onecli.sh/docs#website\",\"name\":\"OneCLI\",\"url\":\"https://onecli.sh/docs\",\"publisher\":{\"@id\":\"https://onecli.sh/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://onecli.sh/docs/integrations/github#webpage\",\"url\":\"https://onecli.sh/docs/integrations/github\",\"name\":\"Let AI Agents Open PRs and Issues on GitHub\",\"description\":\"Connect GitHub with OAuth or a GitHub App so agents can push code, open PRs, and run workflows. Tokens are injected by the gateway, never by the agent.\",\"dateModified\":\"2026-11-03T01:51:11.664Z\",\"isPartOf\":{\"@id\":\"https://onecli.sh/docs#website\"},\"breadcrumb\":{\"@id\":\"https://onecli.sh/docs/integrations/github#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://onecli.sh/docs/integrations/github#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Cloud integrations\",\"item\":\"https://onecli.sh/docs/integrations/apollo-io\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Let AI Agents Open PRs and Issues on GitHub\",\"item\":\"https://onecli.sh/docs/integrations/github\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://onecli.sh/docs/integrations/github#article\",\"headline\":\"Let AI Agents Open PRs and Issues on GitHub\",\"name\":\"Let AI Agents Open PRs and Issues on GitHub\",\"description\":\"Connect GitHub with OAuth or a GitHub App so agents can push code, open PRs, and run workflows. Tokens are injected by the gateway, never by the agent.\",\"url\":\"https://onecli.sh/docs/integrations/github\",\"mainEntityOfPage\":{\"@id\":\"https://onecli.sh/docs/integrations/github#webpage\"},\"dateModified\":\"2026-11-03T01:51:11.664Z\",\"publisher\":{\"@id\":\"https://onecli.sh/#organization\"},\"isPartOf\":{\"@id\":\"https://onecli.sh/docs#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"OneCLI\",\"creator\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","siteName":"OneCLI","nav":{"global":{"anchors":[{"anchor":"GitHub","icon":"https://mintlify.s3.us-west-1.amazonaws.com/chartdbinc/images/github.svg","href":"https://github.com/onecli"}]},"tabs":[{"tab":"Documentation","pages":[{"title":"Documentation","href":""}]},{"tab":"Integrations","groups":[{"group":"Integrations","root":{"title":"Integrations: Connect Agents to External Services","sidebarTitle":"Overview","href":"/integrations"},"pages":[{"title":"App Connections: How OAuth \u0026 API Keys Work","sidebarTitle":"App Connections","href":"/integrations/app-connections"},{"title":"Custom Connections: Connect Any API With a Key","sidebarTitle":"Custom connections","href":"/integrations/custom-connections"},{"title":"Chat With AI Agents and Approve Actions in Slack","sidebarTitle":"Slack","href":"/integrations/slack"},{"title":"Keep LLM API Keys Out of Your AI Agents","sidebarTitle":"LLMs","href":"/integrations/llms"},{"title":"External Vaults: Connect Password Managers","sidebarTitle":"External Vaults","href":"/vaults/overview"}]},{"group":"Cloud integrations","pages":[{"title":"Prospect and Enrich Leads in Apollo.io With Agents","sidebarTitle":"Apollo.io","href":"/integrations/apollo-io"},{"title":"Use AWS From AI Agents Without Exposing Keys","sidebarTitle":"AWS","description":"Let agents call S3, Lambda, EC2, and other AWS APIs while the gateway signs requests with SigV4. Use IAM access keys or a cross-account role.","href":"/integrations/aws"},{"title":"Let AI Agents Open PRs and Issues on GitHub","sidebarTitle":"GitHub","href":"/integrations/github"},{"title":"Org-Approved GitHub Repo Access for AI Agents","sidebarTitle":"GitHub App","description":"Give agents access to only selected repos with a GitHub App. OneCLI mints short-lived installation tokens and injects them, so agents never see them.","href":"/integrations/github-app"},{"title":"Let AI Agents Query Datadog Metrics and Monitors","sidebarTitle":"Datadog","href":"/integrations/datadog"},{"title":"Let AI Agents Update HubSpot CRM Records","sidebarTitle":"HubSpot","href":"/integrations/hubspot"},{"title":"Let AI Agents Triage Sentry Errors","sidebarTitle":"Sentry","href":"/integrations/sentry"},{"title":"Let AI Agents Read and Write OneNote Notebooks","sidebarTitle":"Microsoft OneNote","href":"/integrations/microsoft-onenote"},{"title":"Connect AI Agents to Outlook Mail in Microsoft 365","sidebarTitle":"Outlook Mail","href":"/integrations/outlook-mail"},{"title":"Let AI Agents Book Meetings in Outlook Calendar","sidebarTitle":"Outlook Calendar","href":"/integrations/outlook-calendar"}]},{"group":"All app connections","pages":[{"title":"Connect AI Agents to Affinity CRM With an API Key","sidebarTitle":"Affinity","href":"/integrations/affinity"},{"title":"Let AI Agents Manage Attio CRM Records","sidebarTitle":"Attio","href":"/integrations/attio"},{"title":"Run Clay Enrichment From AI Agents","sidebarTitle":"Clay","href":"/integrations/clay"},{"title":"Query PostHog Analytics and Flags From Agents","sidebarTitle":"PostHog","href":"/integrations/posthog"},{"title":"Connect AI Agents to Salesforce With an External App","sidebarTitle":"Salesforce","href":"/integrations/salesforce"},{"title":"Turn Timeless Meetings Into Agent Follow-Ups","sidebarTitle":"Timeless","href":"/integrations/timeless"},{"title":"Let Agents Search Circleback Meeting Notes","sidebarTitle":"Circleback","href":"/integrations/circleback"},{"title":"Run HeyReach LinkedIn Campaigns From AI Agents","sidebarTitle":"HeyReach","href":"/integrations/heyreach"},{"title":"Automate Dripify LinkedIn Outreach With Agents","sidebarTitle":"Dripify","href":"/integrations/dripify"},{"title":"Let On-Call Agents Triage PagerDuty Incidents","sidebarTitle":"PagerDuty","href":"/integrations/pagerduty"},{"title":"Query Coralogix Logs and Metrics From Agents","sidebarTitle":"Coralogix","href":"/integrations/coralogix"},{"title":"Search Company Knowledge in Onyx From Agents","sidebarTitle":"Onyx","href":"/integrations/onyx"},{"title":"Scoped Cloudflare API Tokens for AI Agents","sidebarTitle":"Cloudflare","href":"/integrations/cloudflare"},{"title":"Set Up One Google OAuth Client for All Google Apps","sidebarTitle":"Google (setup)","href":"/integrations/google"},{"title":"Let AI Agents Search, Draft, and Send Gmail","sidebarTitle":"Gmail","href":"/integrations/gmail"},{"title":"Let AI Agents Schedule Meetings in Google Calendar","sidebarTitle":"Google Calendar","href":"/integrations/google-calendar"},{"title":"Give AI Agents Access to Google Drive Files","sidebarTitle":"Google Drive","href":"/integrations/google-drive"},{"title":"Let AI Agents Draft and Edit Google Docs","sidebarTitle":"Google Docs","href":"/integrations/google-docs"},{"title":"Let AI Agents Read and Update Google Sheets","sidebarTitle":"Google Sheets","href":"/integrations/google-sheets"},{"title":"Generate Google Slides Decks With AI Agents","sidebarTitle":"Google Slides","href":"/integrations/google-slides"},{"title":"Build Google Forms and Read Responses With Agents","sidebarTitle":"Google Forms","href":"/integrations/google-forms"},{"title":"Create Google Meet Links From AI Agents","sidebarTitle":"Google Meet","href":"/integrations/google-meet"},{"title":"Search and Organize Google Photos With AI Agents","sidebarTitle":"Google Photos","href":"/integrations/google-photos"},{"title":"Track To-Dos in Google Tasks From AI Agents","sidebarTitle":"Google Tasks","href":"/integrations/google-tasks"},{"title":"Automate Google Workspace User Admin With Agents","sidebarTitle":"Google Admin","href":"/integrations/google-admin"},{"title":"Pull GA4 Reports Into AI Agents","sidebarTitle":"Google Analytics","href":"/integrations/google-analytics"},{"title":"Let AI Agents Check Indexing in Search Console","sidebarTitle":"Google Search Console","href":"/integrations/google-search-console"},{"title":"Automate Google Classroom Coursework With Agents","sidebarTitle":"Google Classroom","href":"/integrations/google-classroom"},{"title":"Manage YouTube Playlists and Analytics With Agents","sidebarTitle":"YouTube","href":"/integrations/youtube"},{"title":"Let AI Agents Search and Update Notion Pages","sidebarTitle":"Notion","href":"/integrations/notion"},{"title":"Let AI Agents Create and Triage Jira Issues","sidebarTitle":"Jira","href":"/integrations/jira"},{"title":"Give AI Agents Search and Edit Access to Confluence","sidebarTitle":"Confluence","href":"/integrations/confluence"},{"title":"Let AI Agents Manage Your Todoist Tasks","sidebarTitle":"Todoist","href":"/integrations/todoist"},{"title":"Give AI Agents Safe Access to Your Dropbox Files","sidebarTitle":"Dropbox","href":"/integrations/dropbox"},{"title":"Deploy to Fly.io From an Agent Without Exposing Tokens","sidebarTitle":"Fly.io","href":"/integrations/flyio"},{"title":"Let AI Agents Post to LinkedIn on Your Behalf","sidebarTitle":"LinkedIn","href":"/integrations/linkedin"},{"title":"Connect AI Agents to Monday.com Boards","sidebarTitle":"Monday.com","href":"/integrations/monday"},{"title":"Administer MongoDB Atlas Clusters With Agents","sidebarTitle":"MongoDB Atlas","href":"/integrations/mongodb-atlas"},{"title":"Sync Navan Bookings and Expenses With AI Agents","sidebarTitle":"Navan","href":"/integrations/navan"},{"title":"Let AI Agents Send Email With Resend","sidebarTitle":"Resend","href":"/integrations/resend"},{"title":"Send SMS and WhatsApp From AI Agents With Twilio","sidebarTitle":"Twilio","href":"/integrations/twilio"},{"title":"Zendesk Integration: Tickets and Help Center","sidebarTitle":"Zendesk","href":"/integrations/zendesk"},{"title":"Manage Supabase Projects With AI Agents","sidebarTitle":"Supabase","href":"/integrations/supabase"},{"title":"Call Claude and Gemini on Vertex AI From Agents","sidebarTitle":"Vertex AI","href":"/integrations/vertex-ai"},{"title":"Let AI Agents Edit Webflow CMS and Publish Sites","sidebarTitle":"Webflow","href":"/integrations/webflow"},{"title":"Let AI Agents Schedule Zoom Meetings and Get Recordings","sidebarTitle":"Zoom","href":"/integrations/zoom"},{"title":"Give Agents AWS Access With an IAM Role, Not Keys","sidebarTitle":"AWS Role","href":"/integrations/aws-role"},{"title":"Bitbucket Repos, Pull Requests, and Pipelines","sidebarTitle":"Bitbucket","href":"/integrations/bitbucket"},{"title":"Manage Docker Hub Repositories From AI Agents","sidebarTitle":"Docker Hub","href":"/integrations/docker"},{"title":"Read Fathom Meeting Summaries From AI Agents","sidebarTitle":"Fathom","href":"/integrations/fathom"},{"title":"Give AI Agents Access to Fireflies Transcripts","sidebarTitle":"Fireflies","href":"/integrations/fireflies"},{"title":"Let AI Agents Work With GitLab Merge Requests","sidebarTitle":"GitLab","href":"/integrations/gitlab"},{"title":"Send Google Chat Messages From AI Agents","sidebarTitle":"Google Chat","href":"/integrations/google-chat"},{"title":"Let AI Agents Look Up and Update Google Contacts","sidebarTitle":"Google Contacts","href":"/integrations/google-contacts"},{"title":"Let AI Agents Read Your Granola Meeting Notes","sidebarTitle":"Granola","href":"/integrations/granola"},{"title":"Route Agent Package Installs Through JFrog","sidebarTitle":"JFrog Artifactory","href":"/integrations/jfrog-artifactory"},{"title":"Let AI Agents File and Update Linear Issues","sidebarTitle":"Linear","href":"/integrations/linear"},{"title":"Run Snowflake SQL From an Agent, Token Hidden","sidebarTitle":"Snowflake","href":"/integrations/snowflake"},{"title":"Use a Restricted Stripe Key With AI Agents","sidebarTitle":"Stripe","href":"/integrations/stripe"},{"title":"Let AI Agents Manage Trello Boards and Cards","sidebarTitle":"Trello","href":"/integrations/trello"},{"title":"Let AI Agents Deploy and Manage Vercel Projects","sidebarTitle":"Vercel","href":"/integrations/vercel"},{"title":"Let AI Agents Post and Read on X (Twitter)","sidebarTitle":"X","href":"/integrations/x"},{"title":"Let AI Agents Work Zoho CRM Leads and Deals","sidebarTitle":"Zoho CRM","href":"/integrations/zoho-crm"},{"title":"Let AI Agents Draft Word Docs in OneDrive","sidebarTitle":"Microsoft Word","href":"/integrations/microsoft-word"}]},{"group":"LLMs","pages":[{"title":"Connect Claude to Agents With a Token or API Key","sidebarTitle":"Anthropic","href":"/integrations/anthropic"},{"title":"Use OpenAI API Keys and Codex OAuth With AI Agents","sidebarTitle":"OpenAI","href":"/integrations/openai"}]},{"group":"External Vaults","pages":[{"title":"Bitwarden Vault: Sync Secrets to the Gateway","sidebarTitle":"Bitwarden","href":"/vaults/bitwarden"},{"title":"1Password Vault: Service Account Integration","sidebarTitle":"1Password","href":"/vaults/1password"}]}]},{"tab":"Guides","pages":[{"title":"Guides","href":"/guides"}]},{"tab":"API Reference","pages":[{"title":"API Reference","href":"/api-reference"}]},{"tab":"SDKs","pages":[{"title":"SDKs","href":"/sdks"}]}]},"basePath":"","title":"Let AI Agents Open PRs and Issues on GitHub - OneCLI","buildId":"dpl_BSPUBxEoKhhK7HzXVDPxdPvWx4xc","deploymentId":"dpl_BSPUBxEoKhhK7HzXVDPxdPvWx4xc","dynamics":["07c022d89b","a74be98ba7"],"chunks":["Frame-DRxXE_WT.js","DynamicMarkdown-AlxJK8VR.js","zoom-image-lightbox-B_-GSaTf.js","lightbox-handle-r17bVUz3.js"]}