Blog
Notes from the OneCLI team on AI agents, credentials and security.
 · 3 min read
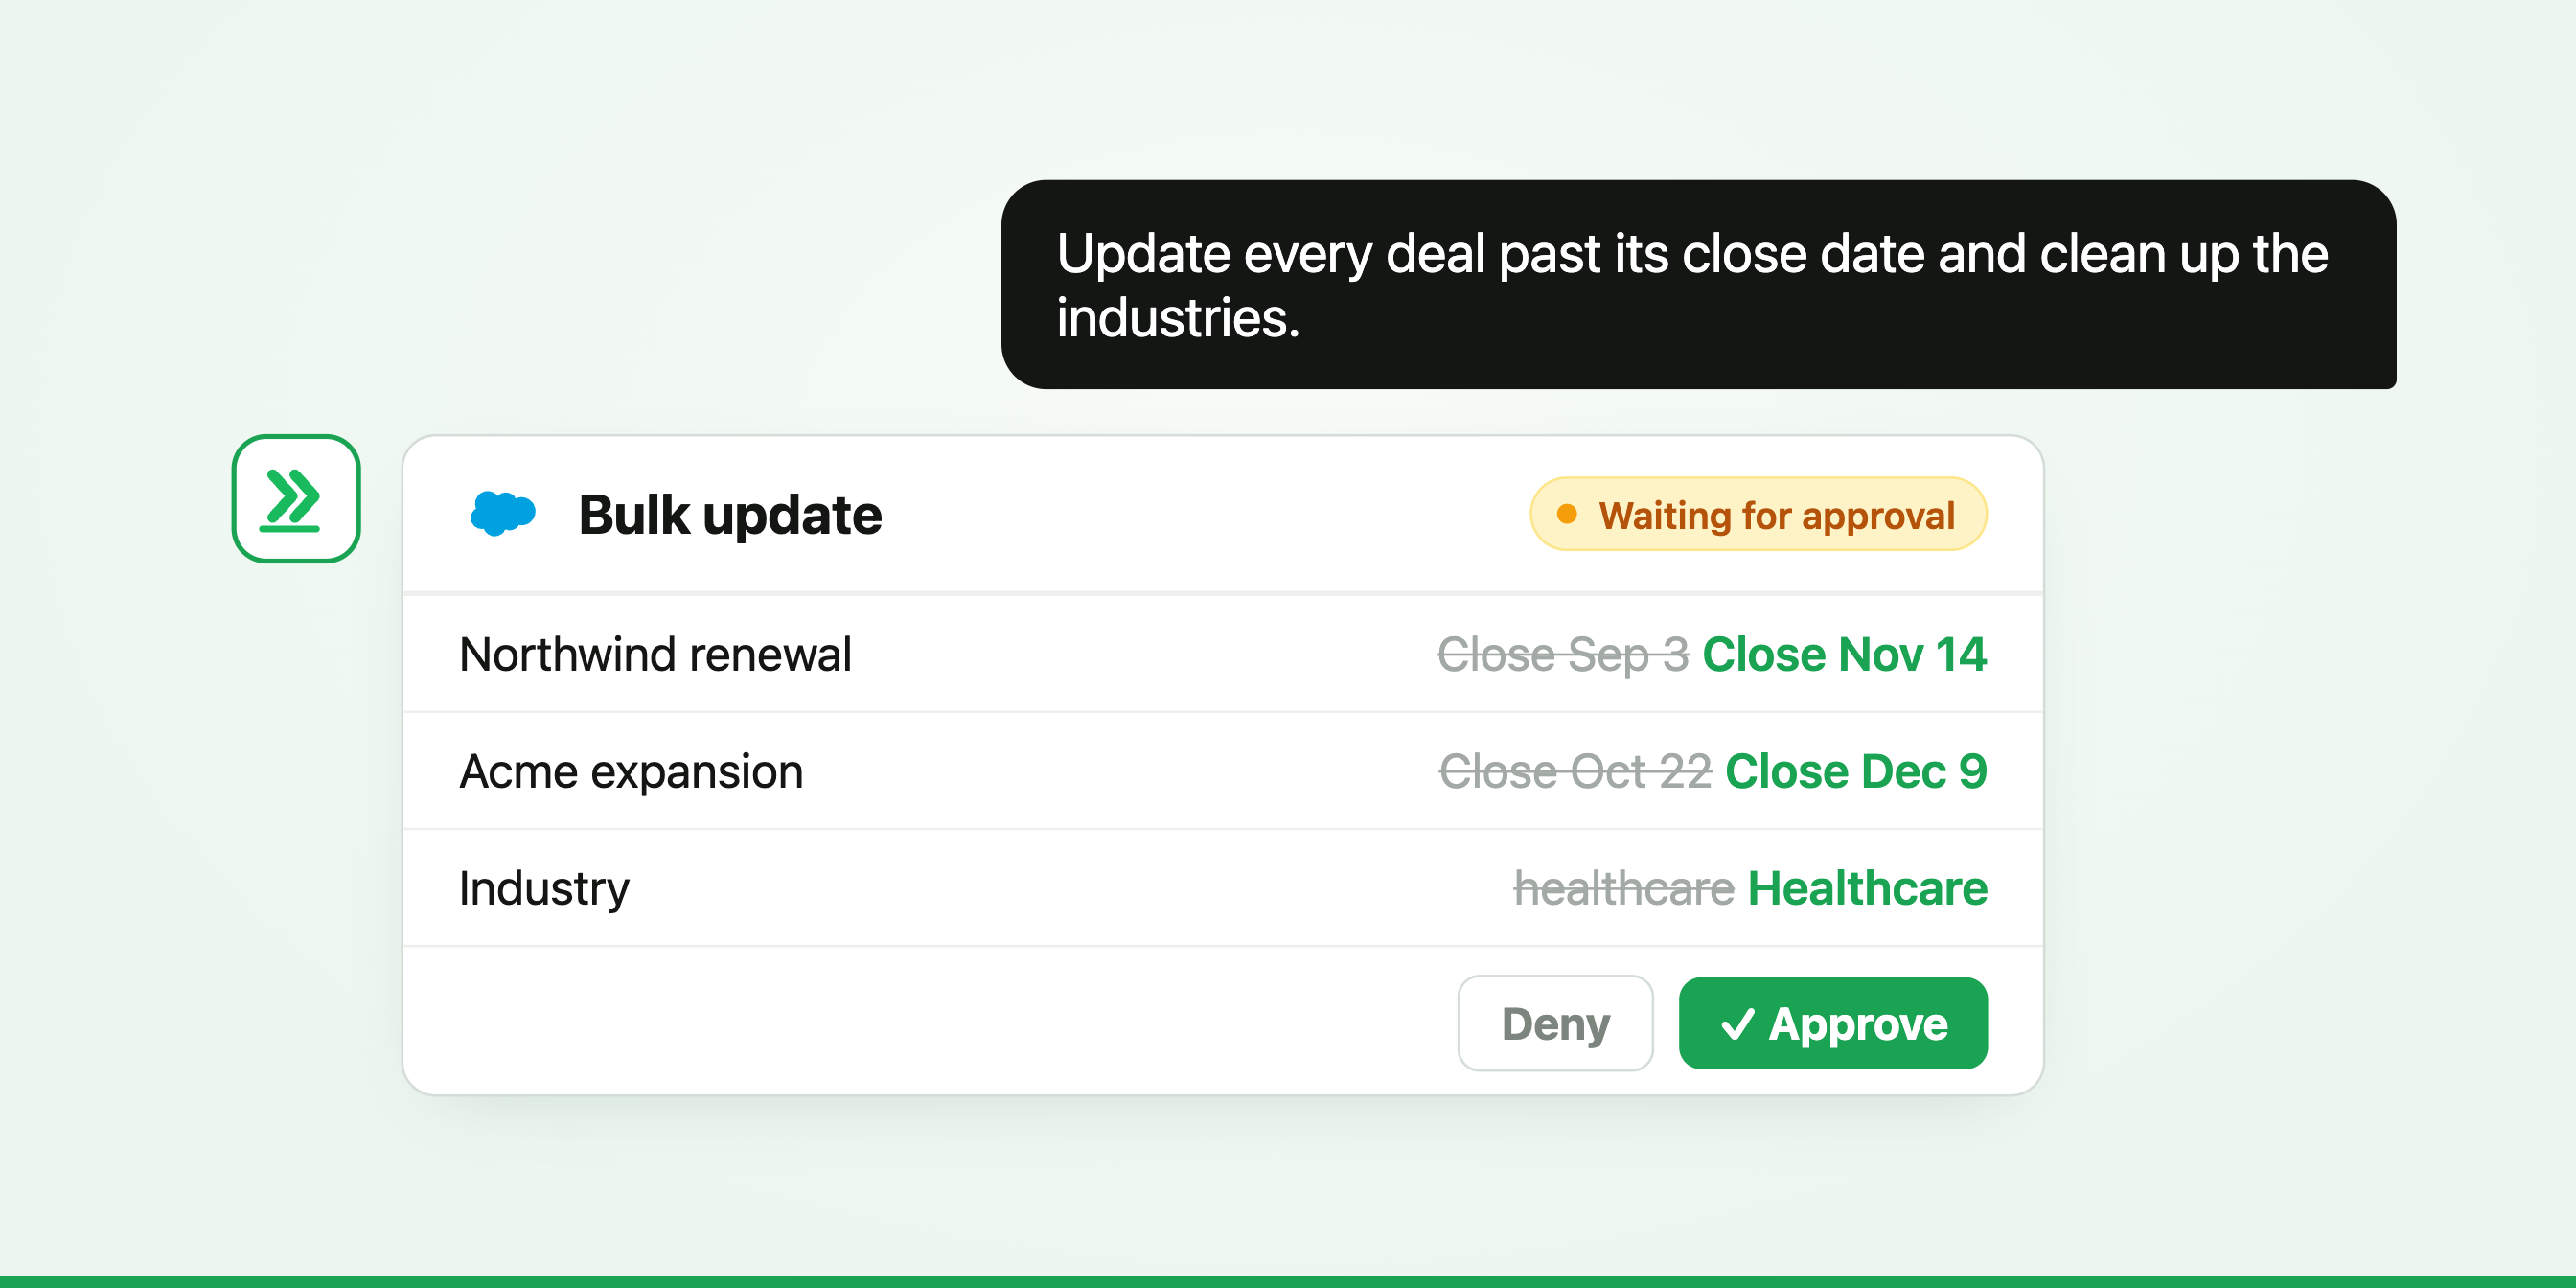
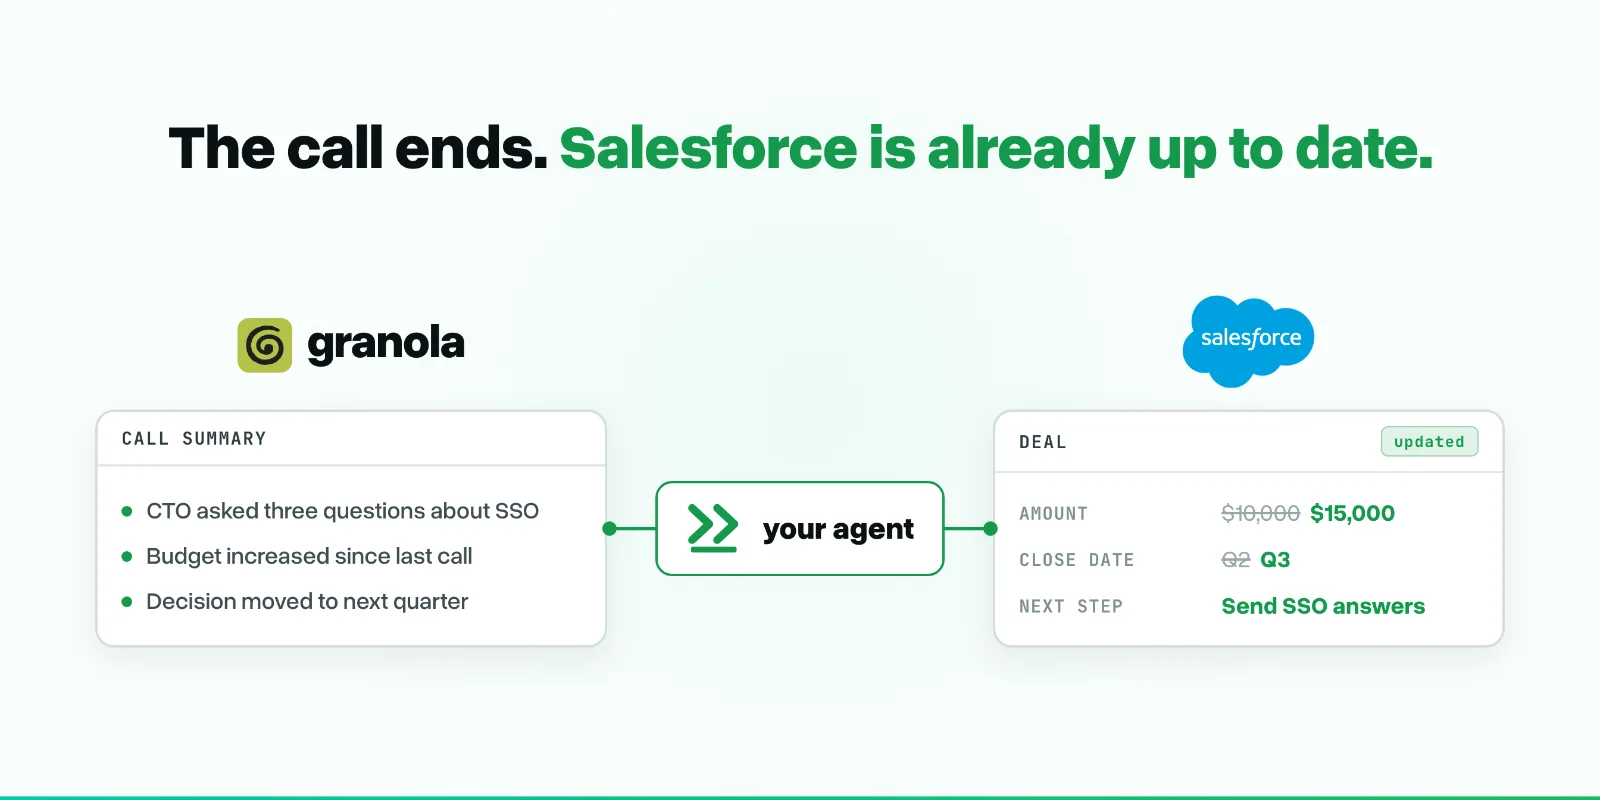
I Taught My Agent to Do the Part of My Job I Kept Skipping
I haven't manually updated a Salesforce record in weeks. Granola had every call, Salesforce had what I remembered, so I handed both to my agent.
 · 4 min read
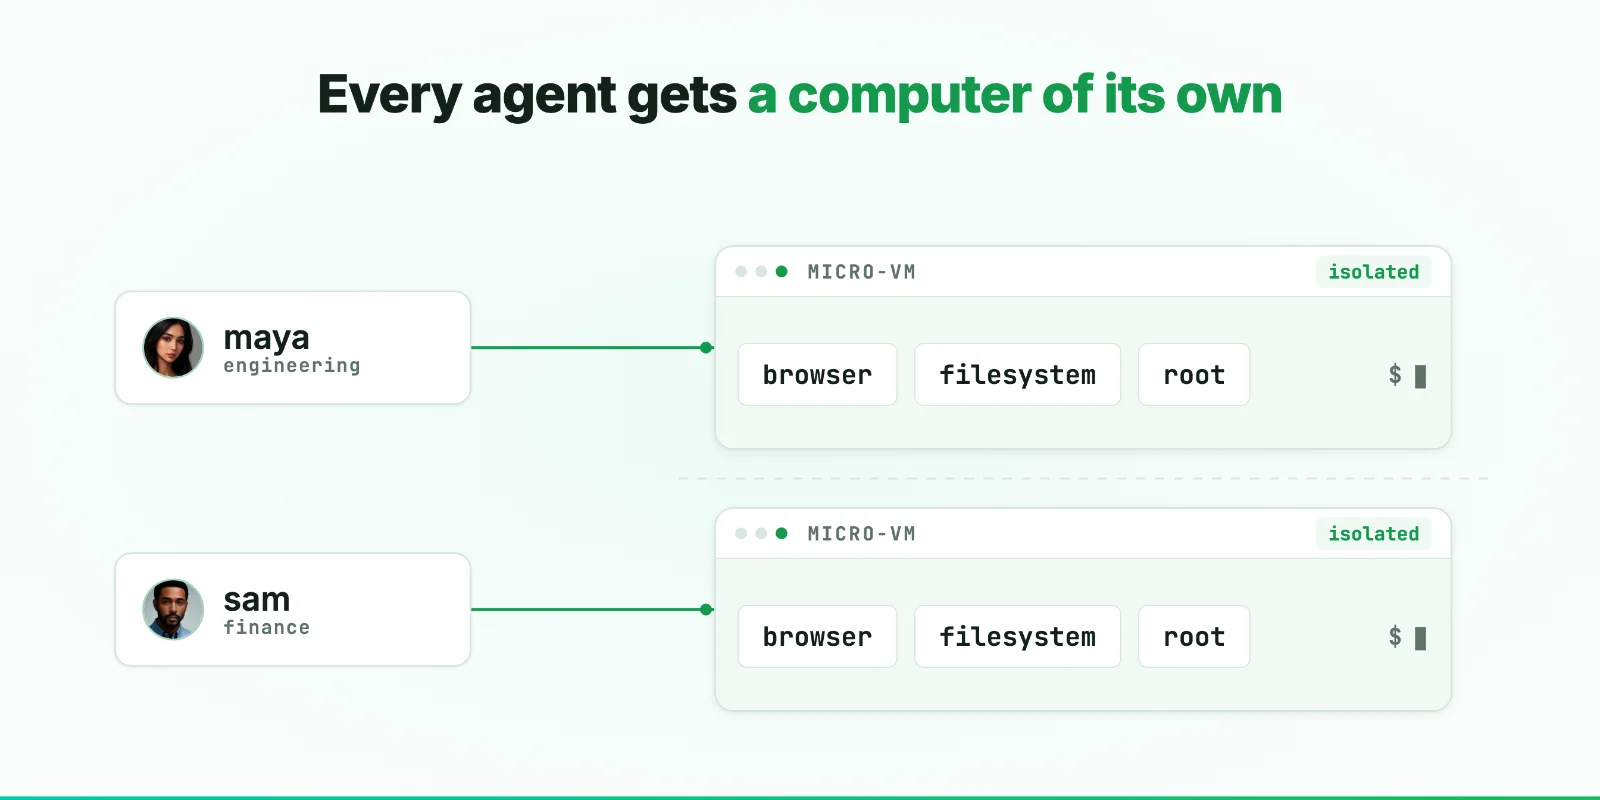
Why We Gave Every Agent a Computer
Containers were enough until agents needed to run full stacks, drive browsers, and test against real providers. So every agent on OneCLI Cloud got its own micro-VM.
 · 5 min read
Every Employee Gets an Agent
OneCLI now ships the agent, not just the layer that keeps it honest: one per employee, scoped passes instead of keys, and one control plane over all of them.
 · 3 min read
OneCLI Is Live on the 1Password Marketplace
OneCLI is now available on the 1Password Marketplace. Vault credentials injected at request time, with runtime policy enforcement.
 · 7 min read
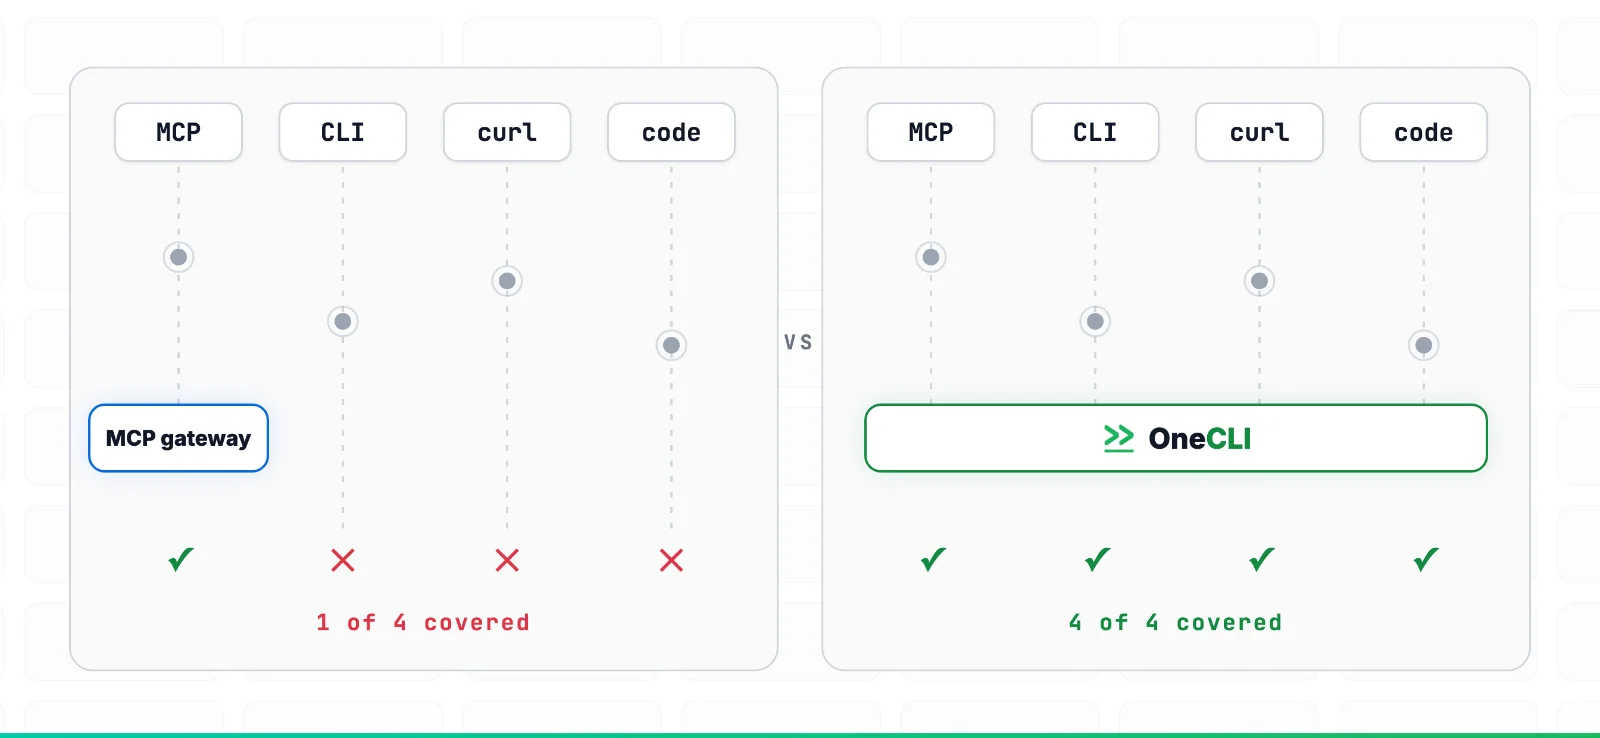
Your MCP Gateway Can't See Most of What Your Agent Does
Agents reach services through CLIs, curl, and generated code, not just tool calls. Guardrails that only cover MCP miss most of that traffic.
 · 3 min read
Bitwarden Integrates with OneCLI Agent Vault
Bitwarden launched their Agent Access SDK with native OneCLI support. Human-in-the-loop approval meets runtime policy enforcement.
 · 4 min read
NanoClaw Now Uses Agent Vault as Its Default Credential Layer
NanoClaw adopted OneCLI Agent Vault for credential isolation across agent groups. What this means and why it matters.
 · 5 min read
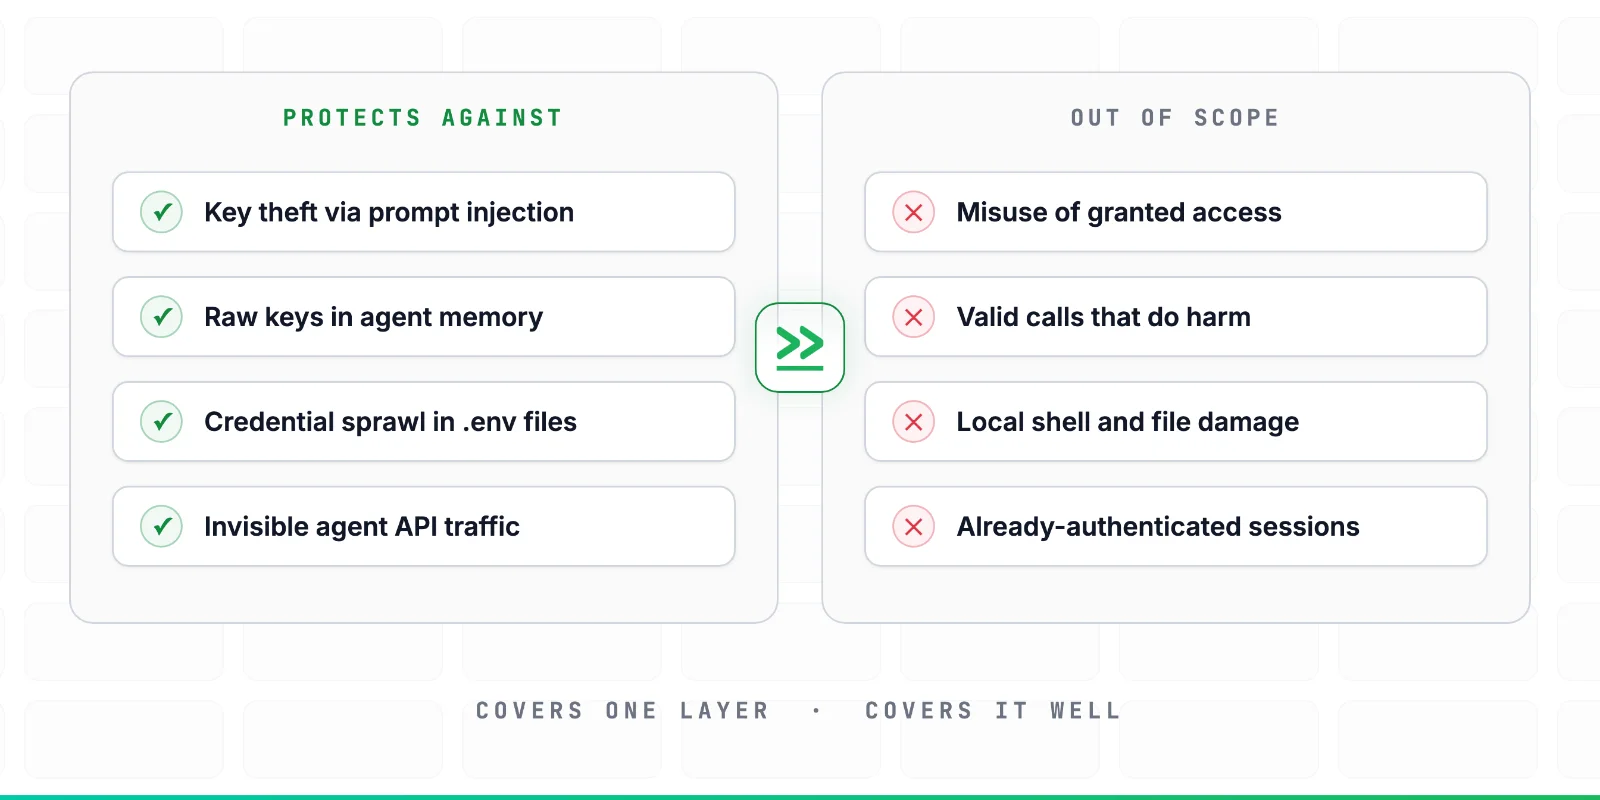
What a Credential Vault Can and Can't Do for AI Agent Security
An honest look at what OneCLI protects against, what it doesn't, and where it fits in a security stack.
 · 2 min read
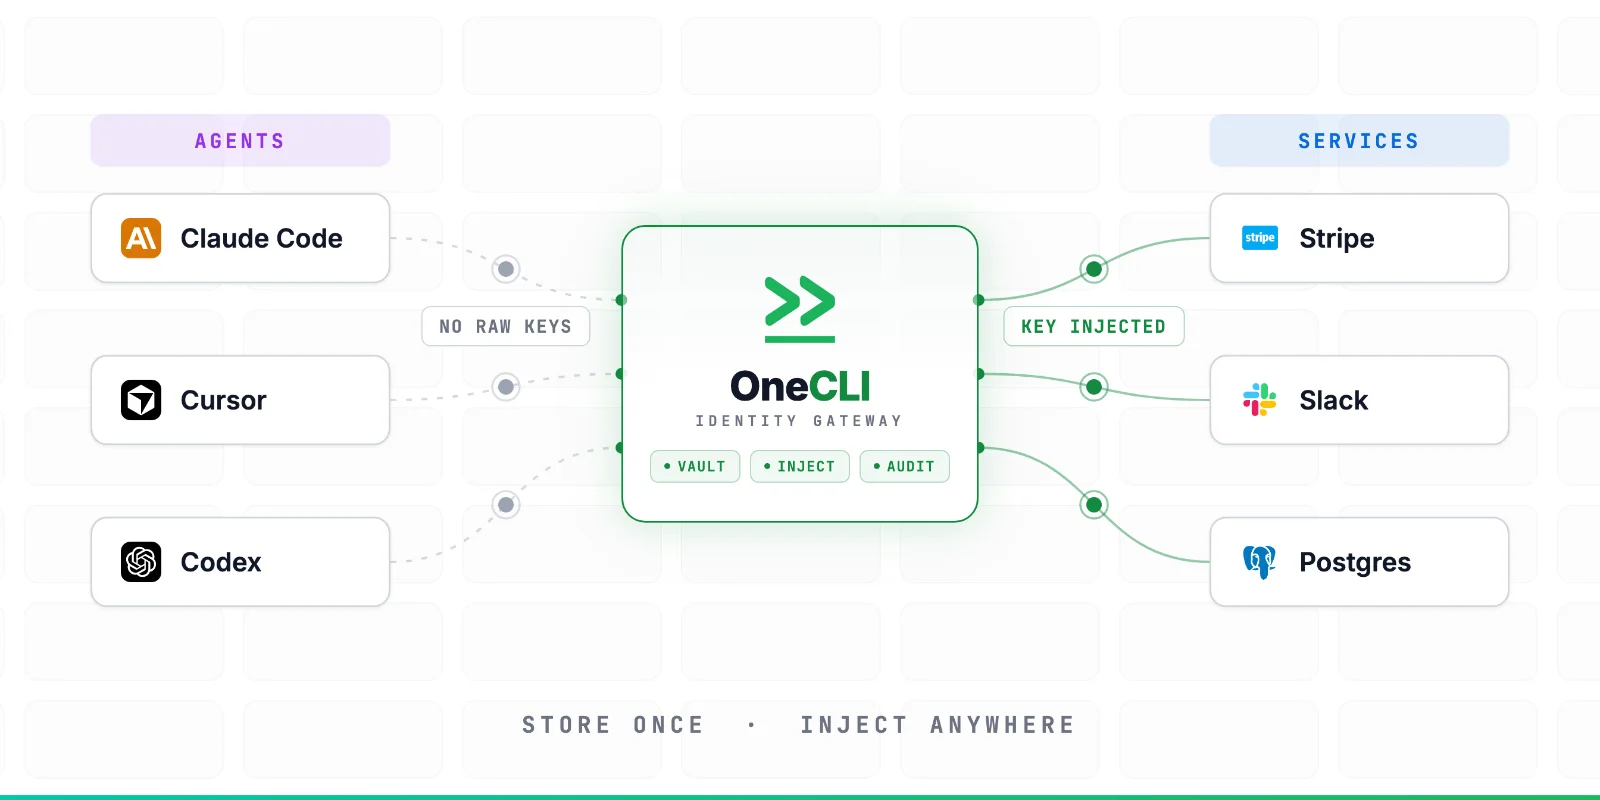
Why We Built OneCLI
The problem with secrets in AI agents, and how we're solving it.